PCI DSS | Requirements And Certification Approach
admin
Sep 29, 2026
- Dec 21, 2021 2:00 PM IST
- English
- Free
 Shares
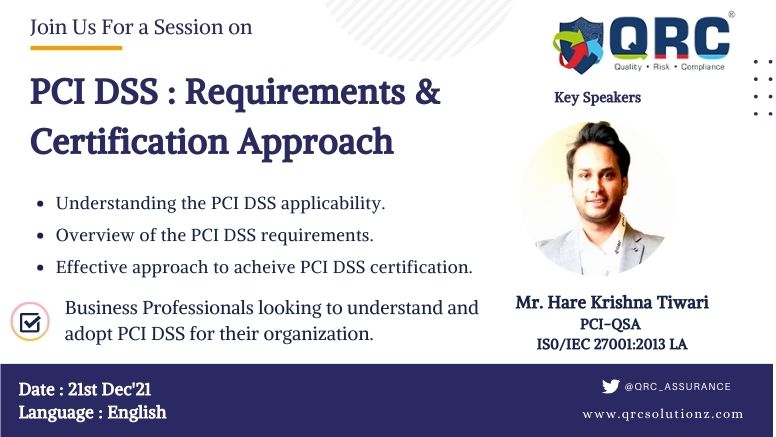
Join us for an informative session on PCI DSS 3.2.1 and understand the requirements and approach necessary to setup security controls to protect sensitive card data and manage compliance.
Who Should Attend?
- CEO, CTO, CISO, Chief Compliance officer
- IT Compliance Head, IT Security Head.
- IT Infrastructure Officer, IT Security Auditor, IT GRC Lead
- Privacy Professionals, Payment Security Professionals, Payment Compliance Officers
Key Benefits:
- Insights of PCI expectations from Approved PCI QSA Company
- No Fees – Only time to invest to gain the knowledge
- Certificate of Completion on successfully attending the session.
- Choosing which approach is best for your organization
- Session at your doorstep.
Audit-Ready PCI DSS
Don’t risk fines. Let our QSA team guide your certification process smoothly.
Request Consultation NDA Available
Other Webinars
 Previous

 Webinar
New Digital Personal Data Protection Bill 2022
An interactive session wherein we will discuss the Terminologies, Data Fiduciary, User Rights, Cross-border data…
Read More Webinar
PCI DSS 4.0 Introduction and New Updates with QnA
Read More Webinar
ISO/IEC 27002:2022 | Understanding the new revisions
Read More Webinar
PCI Software Security Framework | Secure Software LifeCycle
“PCI SSF | Secure Software Lifecycle Overview” is a part of initiative by QRC wherein…
Read More Webinar
Data Privacy Day : Implementing privacy controls ISO 27701
On this Data Privacy Day, we would walk through the newly introduced privacy framework supports…
Read More Webinar
PCI PA DSS to PCI-SSF Transition
“PA DSS to PCI-SSF : Everything that you need to know about the transition” is…
Read More Webinar
SWIFT CSP : Compliance with CSCF v2021
In wake of the rising data breach, the Society for Worldwide Interbank Financial Telecommunications (SWIFT)…
Read More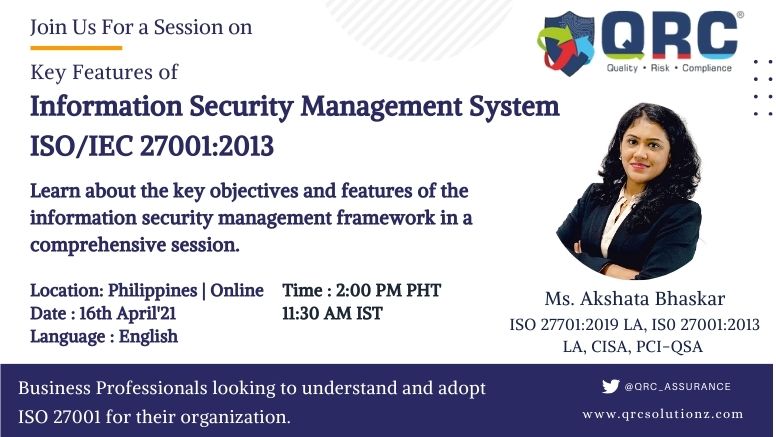 Webinar
ISO/IEC 27001:2013 – Key Features/Benefits
“Information Security Management system (ISMS) ISO/IEC 27001:2013 | Key Features/Benefits” is an FREE Online initiative…
Read MoreReady to become compliant?
Talk to QRC to understand your scope, close gaps, and move confidently
toward validation readiness.