Top 8 Challenges to becoming SOC 2 Certified

SOC 2 on your mind? Here are a few difficult encounters on your journey to be SOC2 compliant

Is your company immune to cybercrimes?

Whether a large corporation, small business, start-up, or government agency, no one is immune to Cyber-attacks! Recent ransomware attacks sent an uninviting reminder of the vulnerability of online security issues. The Denver Post states that 60% of all cyber-attacks are targeted towards small and mid-sized businesses, and stats state that about 4,000 attacks are attempted per day! Small businesses are more at the receiving end due to the ease of penetration.

To such attacks, some businesses may be able to manage the recovery of their losses, but others may not be so lucky. Companies like Medstar Health (a chain of hospitals in Baltimore) entered the crisis after a hacking incident and lost all patients’ data. It had to suffer shutdowns later. Another recent example is one of the nationalized bank incidents where vulnerability puts critical financial and personal information of 180 million customers at risk. Although the bank has assured that customers’ data is not affected, the digital banking information of the bank was compromised with administrative controls. Therefore, Cybersecurity must be taken seriously by organizations. Place stringent compliance measures to avoid hefty fines/damages and assure customers that the supply chains are protected. That is why high-quality audits can protect and ensure good practices.

SOC2 audits are most preferred for such checks, due to the higher standards of controls it sets for mitigating and managing information risks. So, let us see what SOC2 is and how it helps in countering cyber security threats.

What Is SOC 2 Compliance?

SOC2 was developed by ‘The American Institute of Certified Public Accountants (AICPA). It is an audit process that defines standards for managing customer services and data securely. It lays down criteria for regular attestation of the controls in an organization so that there is continual mitigation of risks to demonstrate operating effectiveness. It is more like an assurance to the customers of the business, that there is the secure management of customer data across technical and business areas of the organization. SOC2 intends to give organizations a clear picture of how their data will be managed and handled to work with third-party service providers confidently. Mostly prepared for service organizations, it gives insights into non-financial reporting controls and concentrates on five trust services principles.

The SOC 2 defines criteria for managing customer data based on five “trust service principles”, namely :

  1. Security –  SOC2 requires organizations to have protection against unauthorized access, misuse of the software, system abuse, and theft of data.
  2. Availability –  SOC 2 requires that the service provider warrants service availability and accessibility to its users at all times for operations and use.
  3. Processing integrity –  This principle requires the organizations to complete, valid, accurate, timely, and authorized system processes.
  4. Confidentiality –  Needs the organization to protect confidential information with appropriate control measures.
  5. Privacy –  An SOC 2 compliance provider should develop mechanisms in conformity with privacy notice when collecting, using, retaining, disclosing, and disposing of personal information.

Challenges in the Journey of Being SOC2 Certified

SOC2 is important but challenging too. Here are a few pitfalls that must be thoughtfully handled while working to meet SOC2 compliance.

  1. Defining Scope Of SOC2 Report  SOC 2 Report should cover the systems and services that are in use by the clients and that require assurance. It depends much upon the clients’ expectations. However, client service agreements can be a good starting point for this information. The report usually excludes bespoke client-specific services and the information immaterial to the end-users. The scope should be restricted to systems and data, important for the delivery of services to be audited. Including all your systems in scope may be difficult, therefore, think before including any systems with technologies that will be denounced soon. It exerts unnecessary efforts in maintaining these systems to higher standards. If any of the ‘systems’ are services delivered by third parties, you can use their SOC 2 report.
  2. Balancing Competing Priorities  Business deadlines, customer commitments, ongoing project necessities are a few priorities that cannot stop for an audit process. But the audit itself is an important priority, therefore with an audit execution comes to face many operational issues. Balancing between business commitments and performing gap analysis may become a hard task for organizations undergoing audits. To counter this, the least a company can do is to dedicate individuals or enforce ‘other work’ cutbacks till the audits. Else there will be delays and disappointments from control exceptions in the audit.
  3. Better Insight into Control Requirements  The managers and auditors who write the report may not be the ones who evaluate and remediate compliance lacunae. So all of them together should clearly understand control requirements to avoid chaos and confusion during audit interviews for qualifying in the audit report. An auditor’s proficiency and knowledge should be relied upon to have a clear view of standards and control objectives. They can appropriately project actual and effective controls. Engage with a reputable auditing company that has worked with similar size companies, and is proficient in security experts who can execute an efficient SOC 2 audit process. QRC Solutions’ audit process is easier for your team.
  4. Casual Attitude to Policies and Process  Poor communication of policies and processes with the stakeholders leads to gaps, confusion, and insufficient time to mend loopholes and failure in following the set rules inviting vulnerabilities and security issues. Hence, a proper communication arrangement must be established to educate the participants about the importance of adherence to processes.
  5. Unmitigated Documentation  During the SOC2 audits, it is routine to complete your documentation on infrastructure software data and information. Having your network designs and solution architectures well documented reduces many risk factors. For this reason, include these documents as key requirements for SOC2 audits. Yet, maintaining documentation is often a second thought to many.
  6. Sensible Application of Process and Technology  SOC2 requires an organization to have policies and processes in place. It lays standards for technical solutions to support, laid down policies and processes. But oftentimes, concentration on deploying a technology leads to processes that do not meet the needs of the team but only gratify the need for technology.
  7. Inadequate Groundwork  Performing gap analysis before Type 1 and Type 2 audit periods, help to remediate these gaps. With some amount of scrutiny on control requirements and identifying the processes that cannot stand sturdy over time, you may stand successful in the Type 2 audit period. But an inadequate preparation for the audit may put you in a fix.
  8. Knowing that SOC2 is an ongoing process and practice  Having accomplished a SOC 2 audit report is not just the end. Maintaining a valid SOC 2 needs you to continuously keep yourself audited. Keep reevaluating consistently and enhance your processes and tools.

Wrapping Up

SOC 2 is not about ticking all the checkboxes for compliance. Organizations need to know that it is more about placing sharp policies, and practices to ensure the long-term success of your business. QRC Solutions gives you full-stack security to achieve SOC 2 compliance.

QRC’s continuous compliance monitoring methods and expert team can simplify auditing and security evaluations for you. QRC solutions is a highly recommended SOC2 audit partner. It lays out Quality, Risk, and Compliance services completing 2000 assessments with 250 clients in 25 countries.
Single Sign on Single Solution With Multiple

Ever heard of the term “Password fatigue”? It refers to a condition when people are forced to remember multiple passwords. In a 2014 survey by Intermedia, it was found that an organization provides access to a minimum of 15 applications to each of its employees on an average. This means that every employee of an organization needs to remember 15 different credentials every day. Not only does this create password fatigue for the employees but it also creates various challenges putting the network and organization’s data in a vulnerable position through this cumbersome process. Single Sign-On, referred to as SSO solves this problem effortlessly.

Single sign-on has not only solved the many problems faced by employees but has become an important part of the organization’s security program. It can be described as a software solution that gives users single access to various portals through one login and credentials. By decreasing the number and frequency of login attempts, the number of errors comes down, and eventually, network safety is increased. Along with good network safety, an SSO also brings with it several advantages. Let us get to know a few of them:

Benefits of SSO:

  • Healthy password practices:  The SSO reduces the risk of password fatigue and poor password practices as only a single login attempt are required instead of multiple login attempts. This actually enables users to come up with strong passwords as there is no cumbersome process involved with credentials.
  • Aids compliance process:  We all know that compliance and risk management go hand-in-hand. The SSO aids in maintaining compliance in the organization. There is constant monitoring of access management and it ensures compliance within the organization, thus aiding in better management of cyber risk.
  • Password, and beyond:  The SSO is not just about a single access point and credential management. The right SSO solution can even lead to the elimination of credentials totally, through new advancements like OTP-based login, biometric, etc. Organizations have the option to gain better network security by opting for various techniques like two-factor authentication (2FA), multi-factor authentication (MFA). Such techniques can prove to be a breakthrough to an organization’s cyber security practices.
  • Increased speed:  There is a need for highly efficient systems with high speed in industries such as defense, emergency services, hospitality, medicine, etc. due to the huge amount of operations and the quick nature of work involved. SSO not only saves time from repetitive tasks and prevents errors by providing single access to multiple platforms to a huge amount of employees at the same time, but it also increases the efficiency of their operations by preventing cyber-attacks and intrusions.
  • Increased productivity:  By using the SSO, the complexities of mundane routine tasks like remembering multiple credentials, multiple login attempts due to frequent session time-outs, waiting for support from the IT team, etc. are eliminated and in turn, the speed and productivity of employees increase.
  • Easy usage:  With SSO, there is no worry of having to memorize 10 different credentials for 10 different applications or having to log in 15 times again when a session times out. Users can enjoy real ease of use, which in turn induces better cyber safe practices and behavior.
  • Enabling cyber security in a timely manner:  We are well aware of the kind of sudden surge of pressure that the IT teams had to face during the onset of the COVID 19 pandemic. Due to the contingent nature of arrangements that they had to come up with in a short span of time, the burden on the IT team to provide support increased drastically.

Due to this kind of change in situation and expectations, many IT teams had to compromise on the quality of network security they could provide. It can be said that the importance and highlight on cyber security and data protection saw a sudden fall, especially in a time when it was required the most due to the fact that even day-to-day operations proved to be a herculean task to them with the many limitations the “work-from-home culture” brought in. This problem can be resolved with an SSO solution, as it eliminates most of the troubleshooting process and enables an easier diagnosis that can be taken up on a self-help basis. This way, day-to-day operations can be normalized and data security can be given the due importance it requires.

  • Preventing significant losses:  It is an evident fact that SSO improves network security and decreases the risk of data breaches. Organizations gain by avoiding financial and goodwill loss, which would otherwise be caused through cyber-attacks.
  • User account management:  Not only does it help at times of emergency, but also it maintains an orderly manner of credential management during the onboarding and exit of employees in a normal situation. With the SSO, managing user-profiles and accounts becomes hassle-free, thus breaking down complexities.
  • IT costs:  When the process of login and credential management is simplified, the need for troubleshooting in areas like credential management, help desk support, ticket resolutions, etc. reduces. This way, the organization can reduce IT costs.

Gaining the most of it:

While the SSO can prove to be one solution to multiple issues, an organization looking to implement an SSO must take a few extra steps in order to get the most of it. Let us take a look at what these extra steps are how these small steps can go a long way in extracting the best for the organization:

  • Enforcing strong passwords:  Although it is an SSO that makes the intrusion process difficult and provides better network security, the whole network would be compromised even if an intruder manages to crack one single user credential. This is why the management must always enforce extra-strong password practices for its employees to prevent endangering any user.
  • Caution while choosing an SSO solution:  Choosing the right SSO solution is very crucial as in an SSO, authentication, and access to all the applications or portals of the organization are singular. This means that if one portal is facing an issue, access to the rest of the applications will also be delayed. To avoid this, the SSO solution chosen by the organization must be highly reliable and contingency plans for business continuity must be placed properly.
  • Connected authentication, connected access, and connected risks:  A single intrusion not only means all users are endangered, it also means that all the applications connected through the SSO are also at risk open to the attacker. Just strong password practices are not sufficient to avoid this kind of classic failure situation, selecting a high-quality service provider with high-quality network security goes a long way.
  • Set-up process:  The set-up process for an SSO can be quite time and effort-consuming. The bigger the organization, the more complex the process. Caution must be taken while doing tasks like linking the identity provider to the service provider.

PCI Standards: Picking the Right PCI SAQ

There is a quote by FBI Director, Robert Mueller – “There are two different types of companies in the world: those that have been breached and know it and those that have been breached and don’t know it.”

By just being a little cautious, we can prevent data breaches from causing downstream damages. So, reflect upon whether your systems are safe from cyberattacks? To reduce the risks of compromised data of cardholders, it is important to be PCI DSS compliant and use PCI SAQ.

What is PCI SAQ?

Payment Card Industry Self-Assessment Questionnaire (PCI SAQ) is an authentication tool to understand that merchants and service providers who accept credit/debit card payments are compliant with respect to PCI DSS, through simple questionnaires. The statement after PCI SAQ compliance testifies that your company has complied with necessary security measures and the latest version of the PCI Data Security Standards to keep cardholders’ data safe in your business.

Which PCI SAQ is right for me?

There are different SAQs that member businesses can choose from. How you use card information and how you manage card data decides the SAQ your company should fill. Different SAQs are applicable to a specific payment scenario.

It is important to choose the right SAQ because a wrong SAQ can nullify your compliance efforts and throw your business into bigger risks and breaches.

Every business is different, so every assessment is also different. To know which of the SAQ forms to complete is a challenge for merchants. Although PCI DSS has set up the processes to simplify the assessments, but it may stand as a barrier to some merchants’ motivation to complete the assessment. Companies like QRC Solutions offer facilitated SAQ programs to simply and handle the process for you.

Once you know which SAQ is right, you can complete it without hassles. Here we will try to streamline this concern by discussing each type of SAQ.

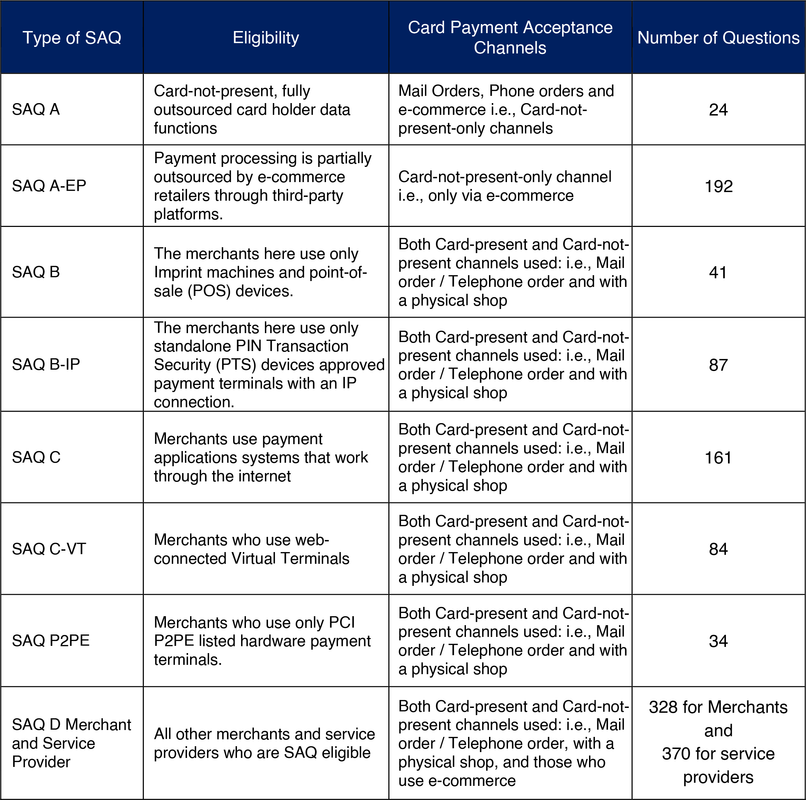
Card Usage Chat

SAQ A

Applies to you when:

  1. Your business operates with “card-not-present” transactions, e.g. eCommerce businesses and mail order/telephone order businesses.
  2. Your company does not handle cardholder data directly. You have outsourced your card handling process completely to a PCI DSS validated by a third party.
  3. The businesses that do not store, process, or transmit cardholder data in systems or premises electronically.

SAQ A-EP

The e-commerce merchants who have moderately outsourced their e-commerce payment channel to PCI-validated third parties qualify for this. They do not electronically store, process, or transmit cardholder data in their business environment.

Applies to you when:

  1. You accept only e-commerce transactions.
  2. Process all cardholder data through an outsourced PCI DSS authorized by the third party.
  3. Your e-commerce websites do not receive cardholder data but control how cardholder data is redirected to a validated third-party payment system. This is a chief argument to be considered when deciding between SAQ A and SAQ A-EP
  4. You have a website hosted by a validated third-party provider.

SAQ B

SAQ B is for merchants who are processing customers’ card information through imprint machines or standalone, dial-out terminals. They can either be card-present, or card-not-present merchants. They do not store customers’ card information on any computer or system.

Applies to you when:

  1. You use only an imprint machine and/or standalone, dial-out terminals via phone line to get customers’ card information.
  2. The standalone dial-out terminals are unrelated to any systems in your company.
  3. The standalone, dial-out terminals are not connected over an internet connection
  4. Your business is not transmitting cardholder data over an internal network or Internet.

SAQ B-IP

This is for merchants who don’t store card data in electronic format. They use IP-connected point-of-interaction (POI) devices. They handle either card-present or card-not-present transactions. They do not store card data on any computer system.

Applies to you when:

  • Your company uses only standalone, PTS-approved IP-connected POI devices to take customers’ card information in your payment processor.
  • Your standalone IP-connected POI devices are listed as authorized, in the PTS POI program
  • Your standalone IP-connected POI is not connected to any systems within your business.

SAQ C

SAQ C is for merchants whose payment applications and POS are connected to the Internet. This can include card-present or card-not-present merchants.

Applies to you when:

  • The business’s payment application and Internet connection are on the same LAN and device.
  • The payment application is not connected to any other systems of your business.
  • The POS is not  for any other locations and the LAN is also for one location only
  • Remember SAQ C does not apply to e-commerce merchants.

SAQ C-VT

This is for merchants processing card information only through standalone virtual payment terminals on a personal computer connected to the Internet.

Applies to you when:

  • The payment processing is done only through a virtual payment terminal which is called up  by an Internet-connected web browser
  • Your virtual payment terminal solution is provided by a PCI DSS authenticated third-party
  • Your company uses a virtual payment terminal solution through a computer that is separated in a single location, and is not connected to other locations or systems within your environment

SAQ P2PE

The P2PE SAQ is applicable to merchants who use a P2PE solution for their payment transactions. This reduces the number of SAQ questions to be filled. (SAQ D requires 329 questions while SAQ P2PE has only 33 questions making compliance easier)

Applies to you when:

  • All payments are processed through a validated PCI P2PE solution ( approved and listed by the PCI)
  • When you store, process or transmit account data only through Point of Interaction (POI) devices validated with PCI-listed P2PE solution
  • When you have implemented controls according to the P2PE Instruction Manual by the P2PE Solution Provider.

SAQ C-VT

This is for merchants who process cardholder data only through isolated virtual payment terminals. This may be on a personal computer on the Internet.

Applies to you when:

  • You use only a virtual payment terminal accessed by an Internet-connected web browser for payment processing.
  • Your business uses a virtual payment terminal solution through an authorized PCI DSS provider
  • You use a PCI DSS-compliant virtual payment terminal solution on a computer that is located remotely in a location not connected to other locations or systems in your business.

SAQ D

SAQ D is for those merchants who don’t meet the criteria for any other SAQ type. Those who store card data electronically and do not use a P2PE certified POS system are covered under this. E.g. Merchants not storing cardholder data electronically, but not meeting criteria of any SAQ type

Service providers qualify for SAQ D, because an institution can both be a merchant and service provider.

QRC is India renowned PCI DSS compliance Services Company spreading across its presence in over 25 countries. Having managed the journey of achieving compliance to maintaining compliance requirements of a company through its lifetime, QRC offers solutions and services to small and big businesses for the Self-Assessment Questionnaire (SAQ) remediation programme also.

Consult the experts today, they will make the process simple and handle the compliance for you.  https://www.qrcsolutionz.com/about-us

ISO/IEC 27001:2013 ISMS: What Is It?

The international standard for information security management is ISO/IEC 27001. It describes how to set up an information security management system that has been independently evaluated and certified. This enables you to secure all financial and private information more effectively, lowering the possibility of unauthorized  access.

With ISO/IEC 27001, you can prove to clients, partners, and other stakeholders that security is crucial to how you conduct business and that you are committed to adhering to international best practises. An Information Security Management System (ISMS) must be established, put into place, maintained, and improved over time according to ISO 27001.

Applicability

ISO 27001 is a standard that is not just relevant to the IT sector. Companies including pharmaceutical firms, healthcare institutions, governmental agencies, and other businesses that might not seem like natural ISO 27001 candidates frequently adopt the standard.

And this is what ISO 27001 is all about: it gives businesses the methodology to identify the risks that could result in events that could happen to them (possible incidents), and then it defines procedures for changing employee behaviour to stop such incidents from occurring.

Why are so many businesses outside of IT interested in ISO 27001? Because, contrary to popular belief, IT is not the most important component in data security. Most of the time, businesses already have all the necessary technology in place, including firewalls, antivirus software, backups, etc. However, since this technology is insufficient, there are still data breaches. This is due to the employees’ lack of knowledge regarding how to utilise the technology securely, but more significantly because the technology is quite limited when it comes to thwarting an insider attack. As a result, it is clear that another strategy is required.

Objective

The following are the goals of ISO 27001 standards:

  • Determine hazards and implement controls to control or eliminate them.
  • The ability to modify controls to only some of your business’s regions or all of them
  • Obtain the confidence of customers and stakeholders that their data is secure
  • Gain preferred supplier status by demonstrating compliance.
  • By displaying compliance, surpass additional tender requirements.

Approach

A five-phase outline of our strategy has been provided. These consist of:

Phase 1: Understand Business Process
Understanding the policies and procedures as well as the management’s expectations and the environment.

Phase 2: Identify Risks and Controls
Determine the target processes and gain an understanding of their flow, risk, information resources, and controls.

Phase 3: Controls Design Testing
Determine the controls based on ISO/IEC 27001, create issue and opportunity registers, test the control architecture, and spot any flaws. Create a plan for risk mitigation and determine the residual risks.

Phase 4: Controls Evaluation
Internally audit your systems to find control flaws and their effects.

Phase 5: Certification
For the certification audit, invite the certification agency.

Cyber security is all about defense and Squid Game

An organization’s network system, attackers with risks awaiting to enter the network and the security team protecting the network. Sounds familiar? Well, it is all the same as the trending South Korean Netflix series “Squid Game”. The series is being widely described as grim, violent, cut-throat, and dystopian, but it can be said that it has been in the No.1 spot in the Top 10 shows in the US, right from September because it is highly relatable. So how is it relatable to today’s cyber security scenario and what are the key takeaways for organizations…?

Read through to find out.

Risk is always uncertain

The first and foremost takeaway from the series can be taken from the first condition the players are exposed to. Nobody amongst the players has an idea about what game they would be part of. They get into the game unaware of what their next game would be like, which denotes how risk is always uncertain. One cannot predict the type of attack they will face or when an attacker is going to try to hack the systems, this is why organizations must always be ready and completely equipped to face the risks.

The attacker is always at an advantage due to this uncertainty of the organization and by being prepared for all types of attacks, organizations can deny the attackers of this advantage.

Timely management of internal threats

The next takeaway can be taken from how internal threats like the police officer Hwang Jun-ho and an organ harvesting team were busted by the game host. We must understand that threats are not only uncertain but also of various types. An organization must tackle attackers with the methods and tools applicable for external threats and must use different strategies for handling internal threats. The network security team of an organization must always be on the lookout for abnormal activities.

Training must be provided to all employees about vulnerabilities like weak password protection, credential sharing, etc. to educate everyone about internal threats and possibilities of the data breaches. Staying fully aware of one’s situation and taking necessary precautions can prove to be useful in handling internal threats.

Being skillful and resourceful

It is to be keenly noted how the players in the Squid Game understand their position quickly and make a strategy for themselves. Right after their first game, they were aware that the sooner they got united the better they could save themselves from being shot dead. By forming a deal between themselves and staying united, they could save themselves from being killed by their peers in the “Midnight Fight”. “Unity is strength” is a time-tested proverb. On realizing that the offender is stronger than the player, the group of people unites and they begin using their skills, their experiences, and their strategies together. This way, they defeat a stronger team in the “Tug of War”.

The attacker always has an edge over the organization due to a wide variety of types of attacks to choose from and the uncertain nature of risks. This is why a network security team of an organization must comprise diverse individuals from various teams. Such a diverse team with diverse knowledge, experience, and point of view together will be able to handle any type of attack irrespective of the uncertainty.  Read more about this: A Go To Guide For Cybersecurity Technique

Opting for the right approach

Selecting the right approach to solving an issue always goes a long way. Consider the example of how a glass manufacturer spots the difference between normal and tempered glass with its reflective property. He further uses this approach to advance in the game with less risk.

Using the right approach has its advantage in dealing with an organization’s security. For each type of threat, a different approach needs to be followed like choosing behavior analysis for internal threats, etc. It is to be noted that once an approach is chosen and practiced and proves successful, documenting it is essential for future usage. Documentation of processes followed each time, creates a record of issues faced and successful methods implemented. This practice of documentation aids in forming company guidelines and that is how best practices evolve within the organization. This way, different approaches to solving an issue can be discovered and the organization becomes more efficient in security management.

Continuous technological improvement:

Just as how time-tested methods, practices, and approaches are important in risk management, being technologically updated and effective usage of tools is equally important. In the Squid Game, tools like knives, lighters throw some light into gaining an early insight into the uncertain and deadly games. This way a few players survive the game.

In cybersecurity, there is a compulsive need to always stay updated with technological tools. Thanks to the nature of risks today, organizations have been enabled to handle every risk through systems right from internal access management to risks associated with external data and its security, which can be evaluated through Vulnerability Assessment and Penetration Testing. The security management team of an organization must deeply reflect upon various factors such as time, cost, and manpower requirements and decide on the purchase of technological updates. If required, redundant or obsolete technology must be completely written off and new purchases must be made on time. To avoid a big gap between an organization’s vulnerabilities and the advantages of attackers, organizations must always stay up to date with their software and risk management tools.

Building a strong defense :

Cyber security is all about defense and it is almost evident at this point how the Squid Game and an organization’s cyber security can be analyzed. Cyber security of an organization must possess a strong defensive approach at all times. In addition to a strong defensive approach, it must also possess a high precautionary approach.

Risk is always better mitigated than managed. Through sufficient precautionary measures, an organization makes it difficult for an attacker to reach the target. When an organization looks sufficiently guarded in the eyes of an attacker, it is less attractive as a target. When an organization is less prospective as a target, an attacker would not choose to intrude on the security of that organization.

This is the crux of the idea behind building a strong defense in cyber security management. We at QRC, provide solutions such as an Enterprise security framework and much more for protecting your organization’s cyber security. Unlike the series, winning the Squid Game will never be a struggle for you.

PIPL: China’s Own Data Security Law For PPI

China has passed the Personal Information Protection Law, referred to as the  PIPL. Currently, the Cybersecurity law protecting cybersecurity, the Data security law protecting data security, and the now the  PIPL  law protecting personal information, consisting of the data protection framework of China.

The  PIPL  will be effective from 1st November 2021, as the first comprehensive law which will remain exclusive to protect personal information. Organizations dealing with personal data related to China will have to comply with the  PIPL. Let us take a look at the highlights of the PIPL law:

PIPL Highlights : Important Definitions

  • 1. Personal Information Processor:  Article 73 defines a Personal information processor as an organization or individual that independently determines the purposes and means for the processing of personal information. “Personal information processor” in PIPL is as “Data controller” is to GDPR.
  • 2. Entrusted Party: Article 21 defines “Entrusted Party” as the entity that processes personal information.
  • 3. Personal Information: Article 4 defines Personal information as any information related to identified or identifiable natural persons recorded by electronic or other means. It is to be noted that anonymized information is not considered personal information under the PIPL.
  • 4. Processing of personal information – It is defined as the  collection, storage, use, processing, transmission, provision, publication, and erasure of personal information.

Cross border transfers

International organizations with business operations in China or Chinese organizations with international operations will have to comply with the cross-border data transfer requirements. The PIPL allows cross-border transfers. The conditions prescribed for cross border transfer are as follows:

  • 1. Article 39  states that the personal information processor must notify individuals about the transfer and obtain separate consent for it.
  • 2. Article 38  states that the personal information processor must ensure data protection measures are provided by the foreign data importer.
  • 3. Article 55  states that the personal information processor must conduct an assessment for the impact of protection of personal information.
  • 4. Article 51  states that there are multiple factors to be considered while designing data protection measures, like defining the objective and framework for processing personal information, classifying the types of information, probability of risk, and infringement of an individual’s rights and interests.

Data protection measures prescribed by the PIPL are as follows:

  • 1. Preparation of operational procedures and internal management system
  • 2. Classifying the personal information with proper classification.
  • 3. Usage of data security tools like encryption.
  • 4. Allocating clearly defined authority to process personal information.
  • 5. Providing training for the employees at regular intervals.
  • 6. Staying prepared with an emergency plan of action for security incidents.

Although the PIPL SCC has not been released, organizations can still choose to obtain a personal information protection certification or to enter into an agreement with the foreign data importer. It is evident from the cross-border data transfer requirements prescribed by the PIPL, that data security is viewed as a matter of national security.

A short review of rights under the PIPL  :-The PIPL law is majorly aligned to the requirements of the GDPR when it comes to personal information rights. Although the extent of implementation of the rights under the PIPL cannot be determined at present, the below rights of the PIPL can be compared to the rights of the GDPR :

  • 1. Right to information
  • 2. Right to access
  • 3. Right to correction or rectification
  • 4. Right to erasure
  • 5. Right to object to and restrict the processing of an individual’s data
  • 6. Right to data portability, complying with the requirements of the Cyberspace Administration of China.
  • 7. Right not to be subject to automated decision-making
  • 8. Right to withdraw consent
  • 9. Right to lodge a complaint with the regulator

A look at the penalties for non-compliance

Let us take a look at the scenario of non-compliance :

  • 1. Article 66 –  A fine of up to 50 million RMB can be issued as per Article 66. Any illegal income will be confiscated and a fine of 5% of the organization’s annual revenue(previous financial year).
  • 2. Article 67 –  Apart from the monetary fine, the violations will be recorded into “credit files” as per China’s national social credit system.
  • 3. Article 69 –  In case of infringement of rights and interests of personal information, tort damages will be levied for the organization.
  • 4. Article 70 –  In case of infringement of rights and interests of personal information of a large number of individuals, public interest lawsuits can be filed under the People’s Procuratorate.

PIPL vs GDPR

When discussing Data security laws, one more major name that arrives in the discussion is the GDPR law. Although it can be said that the PIPL has emerged drawing a few significant influences from the GDPR law, it is different from the GDPR in many ways. Let us look into a few notable differences between the  PIPL  and the GDPR law:

  • 1. Terminologies –  There are many differences in terminologies used in both laws. A few inferences are – “data subjects” in GDPR and “individuals” in PIPL, “data controllers” in GDPR and “personal information handlers” in PIPL, “data processors” in GDPR, and “entrusted parties” in  PIPL.
  • 2. Penalty –  The penalty levied by the  PIPL  is up to 5% of annual revenue. The law does not mention if the penalty is on annual revenue in China or worldwide. The penalty levied by the GDPR is 2% and 4% of annual revenue worldwide.
  • 3. Data breach notification –  In case of a data breach, the  PIPL  does not provide any deadline to issue a notification. The notification must be immediate whereas the GDPR specifies a deadline of 72 hours.
  • 4. Sensitive data –The definition of sensitive data differs between the  PIPL  and GDPR. There might be instances where the same data is classified as sensitive under the  PIPL  and not the GDPR law.

Conclusion

It is now evident that the time has arrived for companies dealing with personal information and data subjects, as China has an exclusive law for data protection. It would be the most appropriate decision to utilize this time and align the data and compliance policies of your organization in line with the PIPL. When implementing the requirements for PIPL, one must have a deep understanding of the existing requirements of the GDPR law implemented in the system.

As mentioned earlier, the PIPL has emerged drawing a few significant influences from the GDPR law. So it would be wise to go ahead with an analysis of the differences between the requirements of both these comprehensive data security laws to save time in transitioning the process differences and in avoiding penalties.