Understanding OSI layers from Security View – Introduction

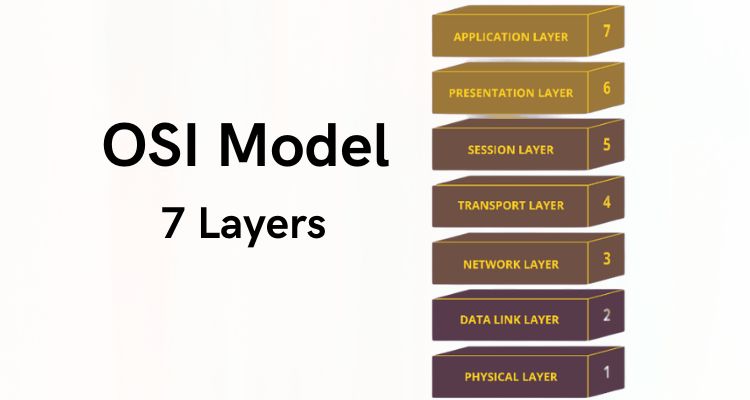
The OSI model, or the Open Systems Interconnection model, is a conceptual framework that standardizes and describes the functions of a communication system. It was developed by the International Organization for Standardization (ISO) in the late 1970s to facilitate interoperability between different computer systems and networks. The OSI model is composed of seven distinct layers, each serving a specific purpose and responsible for a particular aspect of data communication. These layers work together to enable communication between devices and ensure that data is transmitted accurately and efficiently across a network.


Let’s briefly explore each layer:

  1. Physical Layer: This is the lowest layer of the OSI model and deals with the physical transmission of data over a communication medium. It defines the electrical, mechanical, and physical specifications required to establish and maintain a physical link between network devices.
  2. Data Link Layer: The data link layer provides a reliable point-to-point connection for data transmission. It handles error detection and correction, as well as data framing, addressing, and flow control. Ethernet and Wi-Fi are examples of data link layer protocols.
  3. Network Layer: The network layer is responsible for the routing and forwarding of data packets across different networks. It determines the optimal path for data transmission, performs logical addressing, and handles congestion control. IP (Internet Protocol) is a widely used network layer protocol.
  4. Transport Layer: The transport layer ensures reliable and transparent end-to-end data transfer between hosts. It establishes connections, segments data into smaller units, manages flow control, and provides error recovery mechanisms. TCP (Transmission Control Protocol) and UDP (User Datagram Protocol) are common transport layer protocols.
  5. Session Layer: The session layer establishes, maintains, and terminates connections between applications on different network devices. It enables synchronization, checkpointing, and recovery of communication sessions.
  6. Presentation Layer: The presentation layer is responsible for data representation, encryption, compression, and formatting. It ensures that data from the application layer is properly formatted and compatible with the receiving device.
  7. Application Layer: The application layer is the topmost layer and interacts directly with end-user applications. It provides network services and supports protocols for specific applications, such as HTTP (Hypertext Transfer Protocol) for web browsing and SMTP (Simple Mail Transfer Protocol) for email.

By dividing the network communication process into these seven layers, the OSI model allows for modular design, easier troubleshooting, and the ability to replace or upgrade individual layers without affecting the entire system.

Understanding the OSI model and its layers is crucial for network administrators, engineers, and anyone involved in designing, implementing, or troubleshooting computer networks. It provides a common reference point for communication protocols and helps ensure interoperability in complex network environments.

IRDAI Issues Revised Information and Cyber Security Guidelines’23

The Insurance Regulatory and Development Authority of India (IRDAI) recently issued revised Information and Cyber Security Guidelines “IRDAI Information and Cyber Security Guidelines” on 24th April 2023.These guidelines refer to the wide-spread adoption of digital technologies and the concurrent increase in cyber security incidents. The revised guidelines are aimed at enabling the insurance industry to strengthen their defenses as well as related governance mechanisms to deal with such emerging cyber threats.

It indicates that all Insurers including FRBs, Insurance Intermediaries covering Brokers, Corporate Agents, Web Aggregators, TPAs, IMFs, Insurance Repositories, ISNP, Corporate Surveyors, MISPs, CSCs and Insurance Information Bureau of India (IIB) shall adhere to these guidelines. Those entities who have already completed the security audit for FY 2022-23 shall ensure compliance with these guidelines from next financial year.

Read the Complete Guideline here : IRDA Information and Cyber Security Guideline 2023

The IRDAI has taken a proactive step in issuing these revised guidelines to ensure that the insurance industry is well-equipped to deal with the increasing threat of cyber-attacks. It is important for all entities in the insurance industry to adhere to these guidelines and take necessary measures to protect themselves and their customers from cyber threats.

Key Highlights of IRDAI Information and Cyber Security Guidelines, 2023

  • The new guidelines are aimed at improving the cybersecurity practices of insurance companies and intermediaries
  • Primary objective of the guidelines is to bolster the industry’s defenses against cyber threats and enhance its governance mechanisms.
  • Insurers and intermediaries are mandated to deploy suitable security controls, prepare incident response plans, and conduct frequent security audits. The guidelines stress the significance of adopting a risk-based approach to information and cyber security.
  • Entities that have undergone a security audit for the fiscal year 2022-23 must ensure that they comply with the guidelines from the upcoming financial year.

One of the guidelines states that third-party entities are allowed to access an insurance company’s internal systems solely for viewing purposes. This includes accessing data, proposals, and reports, but not uploading or editing any information. They are only permitted to view products, proposals, documents, and reports. Another guideline specifies that entities that store an insurer’s non-public data, including policyholder and investment information, should not have authorization to access the insurer’s systems for the purpose of editing or maintaining such data.

By adhering to these guidelines, companies can ensure that they are taking all necessary steps to protect themselves and their customers from cyber-attacks. This includes implementing strong security measures such as firewalls and encryption, regularly updating software and systems, and training employees on cyber security best practices.

To ensure the security and confidentiality of sensitive data and to mitigate potential cyber threats, all insurance companies and intermediaries must adhere to these guidelines. If an entity has already undergone a security audit for the fiscal year 2022-23, they are obligated to comply with these guidelines starting from the following financial year.

According to recent statistics, among the 829 million cyber-attacks detected and blocked globally by a firm in the fourth quarter of 2022, close to 59 per cent were directed towards India.

As Stephane Nappo said: “Cyber-Security is much more than a matter of IT. It is essential for all entities in the industry to take necessary measures to protect themselves and their customers from cyber threats.

In today’s digital age, cyber security is a major concern for all industries, including the insurance industry. With the increasing use of digital technologies and the growing threat of cyber-attacks, it is essential for companies to have robust cyber security measures in place.  The IRDAI’s revised Information and Cyber Security Guidelines provide a framework for companies in the insurance industry to strengthen their defenses against cyber threats. It is essential for all entities in the industry to adhere to these guidelines and take necessary measures to protect themselves and their customers from cyber threats.

BFSI: PCI and other Regulatory Requirements

The banking industry is undergoing a digital transformation, with more and more financial transactions taking place online and an increasing volume of sensitive financial data being handled by banks. This shift towards digital banking has brought about many benefits, such as increased convenience and accessibility for customers, but it has also introduced new challenges, particularly in terms of cyber security.

To address these challenges, the Reserve Bank of India (RBI) has recently released new guidelines for cyber security for banks operating in India. These guidelines aim to strengthen the security infrastructure of banks and protect sensitive financial information from cyber threats. Compliance with these guidelines is mandatory for all banks and failure to do so may result in penalties and fines. Some of these circulars referred below for the reference. Please note that, these circulars might be got revised later years, without intact the original requirements.

Regulator Subject Circular Number
RBI Storage of Payment System Data DPSS.CO.OD.No 2785/06.08.005/2017-18 dated April 06, 2018,
RBI Guidelines on Regulation of Payment Aggregators and Payment Gateways DPSS.CO.PD.No.1810/02.14.008/2019-20 March 17, 2020 (Annexure 2)
RBI Cyber Security Framework in Banks DBS.CO/CSITE/BC.11/33.01.001/2015-16 June 2, 2016
RBI Master Direction – Information Technology Framework for the NBFC Sector Master Direction DNBS.PPD.No.04/66.15.001/2016-17 June 08, 2017
RBI Guidelines on Information security, Electronic Banking, Technology risk management and cyber frauds DBS.CO.ITC.BC.No. 6/31.02.008/2010-11 April 29, 2011
RBI Master Direction on Digital Payment Security Controls DoS.CO.CSITE.SEC.No.1852/31.01.015/2020-21 February 18, 2021
RBI Basic Cyber Security Framework for Primary (Urban) Cooperative Banks (UCBs) DCBS.CO.PCB.Cir.No.1/18.01.000/2018-19
RBI Master Direction – Information Technology Framework for the NBFC Sector DNBS.PPD.No.04/66.15.001/2016-17 June 08, 2017
RBI Membership of Credit Information Companies (CICs) DBR.No.CID.BC.60/20.16.056/2014-15 January 15, 2015

In addition, the Indian government has also enacted Digital Personal Data Protection Bill, 2022, which lays down the framework for protection of personal data of individuals and makes it mandatory for organizations to comply with it. Banks are also under obligation to comply with the bill.

To meet most of the Security requirements and best practices mentioned in the above guidelines, as a starting point, banks may take some of the global standards/frameworks for implementation such as PCI DSS, ISO 27001 Etc., to protect sensitive customer information and ensure compliance with industry standards and regulatory requirements.

  • PCI DSS (Payment Card Industry Data Security Standards) is a set of security standards that apply to organizations that accept credit and debit card payments. Compliance with these standards is mandatory for all banks that accept card payments and failure to do so can result in significant fines and penalties.
  • ISO 27001 is an information security management standard that outlines the requirements for an information security management system (ISMS). Compliance with this standard demonstrates a commitment to protecting sensitive information and managing risk effectively.
  • In addition to these specific compliance requirements, it is also important for banks to implement good cyber security practices to protect against a wide range of potential threats. This includes activities such as regular security testing, incident response planning, and employee education and awareness programs.

Not meeting these compliances can put the bank at significant risk. Failure to comply with PCI DSS can result in significant fines and reputational damage, while a lack of an effective ISMS can lead to data breaches and loss of sensitive customer information. Inadequate cyber security practices can also lead to costly data breaches and loss of customer trust.

Role of the C-Level Management:

As a CISO or CIO of a bank, the protection of sensitive customer information and compliance with industry standards and regulatory requirements is of the utmost importance. One of the keyways to ensure this is through compliance with PCI DSS, ISO 27001 and implementing good cyber security practices.

Key message for CISOs and CIOs to consider when implementing compliance with PCI DSS, ISO 27001 and good cyber security practices include:

  • Compliance is not optional it is mandatory for maintaining the safety and security of customer data
  • By implementing these standards, you are demonstrating a commitment to protecting sensitive information and managing risk effectively
  • Regular security testing, incident response planning, and employee education and awareness programs are essential for maintaining good cyber security practices

As a CISO or CIO, it is important to take a proactive approach to compliance and implement regular security testing, incident response planning, and employee education and awareness programs to ensure that the bank’s information and assets are protected.

To achieve these compliances, the bank’s higher management should take the following additional activities:

  • Regularly conduct Risk Assessments and Gap Analysis
  • Implement Information Security Risk Management.
  • Regularly conduct penetration testing and vulnerability assessment
  • Regularly conduct security training for employees
  • Implementing a robust incident response plan
  • Regularly conduct internal and external audit.

In conclusion, compliance with PCI DSS, ISO 27001 and good cyber security practices is essential for protecting sensitive customer information and maintaining the safety and security of the bank’s infrastructure.

Scope of PCI DSS in General Banking Environment:

The Payment Card Industry Data Security Standards (PCI DSS) applies to all organizations that accept, process, store or transmit credit card information. Banks are required to comply with the PCI DSS to protect sensitive customer information and ensure the security of cardholder data.

In a bank, the major function that handles credit and debit card information is typically the card services, payment processing, Back Office etc. This services responsible for storing, transmitting, and processing card-related data.

The following areas, functions, and processes within a bank should be compliant with PCI DSS:

  1. Cardholder data environment (CDE): This includes all systems and networks that store, process, or transmit cardholder data, including servers, databases, applications, and point-of-sale terminals.
  2. Network infrastructure: This includes routers, switches, firewalls, and wireless networks that are used to connect the CDE to the rest of the bank’s systems and networks.
  3. Security controls: This includes firewalls, intrusion detection and prevention systems, and other security devices that are used to protect the CDE from unauthorized access.
  4. Access controls: This includes procedures for controlling access to the CDE, such as user authentication and authorization, and physical security measures to prevent unauthorized access to the CDE.
  5. Vulnerability management: This includes regular vulnerability scans, penetration testing, and vulnerability management to identify and remediate vulnerabilities in the CDE.
  6. Incident response: This includes incident response procedures that are in place to handle security breaches and other security incidents.
  7. Compliance and reporting: This include regular compliance testing and reporting to ensure that the bank is in compliance with the PCI DSS.

The new guidelines underscore the importance of digital transformation and the need for banks to take proactive measures to protect their customers’ information. Banks must now invest in advanced technology and security systems to safeguard the increasing volume of financial data they handle. This includes implementing multi-factor authentication, encryption, and intrusion detection systems, as well as regular security audits and assessments.

How QRC Can support Banks to meet these requirements:

  1. Being a PCI QSA Company, QRC support banks to Attain, Maintain, Retain PCI Compliances.
  2. Being a Cert-In Empanelled vendor, QRC Perform all types of Security Configuration Audits, Perform Vulnerability and Penetration testing on all bank critical assets like Networks, Servers, Applications and Other security Solutions.
  3. Having Qualified CISA Auditors, we can perform Information Systems and Cyber security assessments for the bank as per the requirement.
  4. Being a ISO Certification body, QRC Can Perform ISO 27001, ISO 27701 standards assessment and certify the banks for these compliances.
  5. QRC Can deploy proprietary GRC Platform called QRCAssist, for Managing all Compliances and effectively monitor the projects at levels within the Banks. Which also helps the banks to manage their day to day security functions and all audit data can be managed centrally.

In terms of PCI DSS Compliance QRC can support in the ways:

  1. Guiding Bank to determine the PCI DSS Scope and document the Card Data Flows.
  2. Perform readiness assessment w.r.t. PCI DSS Standard and Identify the gaps.
  3. Provide Remediation Plans for closing the Gaps
  4. Remediation Support while implementing PCI DSS Controls within the Banking environment.
  5. Conducting PCI Trainings for stakeholders
  6. Performing VA and PT and Application Security Testing
  7. Help the process owners to document required Policies, Procedures
  8. Perform PCI DSS Final Assessment and Issue the PCI DSS Certification.

The digital transformation of the banking industry is here to stay, and it is vital that banks take the necessary steps to protect their customers’ information. By complying with the RBI’s guidelines and investing in advanced security systems, banks can ensure the safety and security of their customers’ financial data and maintain their trust in the digital age.

From Start-up to Maturity – Building an Ecosystem

As is quite evident, the turn of the 21st Century has seen an extensive turnaround in attitudes and business practices. The corporate world also underwent a paradigm shift, and as a consequence, start-ups started popping up around the world.

There happens to be a fresh crop of enthusiastic founders and creative heads eager than ever to discover a ground-breaking product that would likely be a market hit bringing bouts of revenue. However, solely catering to revolutionary ideas and concepts is of no importance. Setting up a system to bring the concepts to action is what entrepreneurs look forward to.

Entrepreneurs require a cooperative and responsive working body on which they could rely to launch their start-ups not only for the betterment of the local economy but also for the general well-being of society.

Before learning how an ecosystem moves from start-up to maturity, let’s first dig into what a start-up ecosystem is.

Start-up Ecosystem: What Actually is it?

Building up a business empire has no linear way to its inception. The process incorporates various milestones to finally reach a point. Business start-ups too exist like that! Start-ups can’t eke out a solitary living, they are bound to be a part of a larger working system, networked to multiple other start-ups.

Entrepreneurs are backed by an extensive community of organizations, the general public, and other start-up ventures related to them. This co-existence of multiple working bodies is known as a Start-up Ecosystem.

Definition

The know-it-all, Wikipedia defines the start-up ecosystem as “An ecosystem formed by people, start-ups in their various stages and various types of organization in a location (physical or virtual), interacting as a system to create and scale new start-up companies”.

The Concept

The start-up ecosystem works upon the concept of “symbiotic association”. A start-up ecosystem functions on the principles of co-existence and interdependence. One entity of a start-up ecosystem can’t be independent of other members in the association.

The concept materializes upon the inception of a highly intertwined community with a shared pool of resources and cooperation.

Elemental Composition of Start-up Ecosystem

A start-up ecosystem has to pass through various developmental stages to finally make up the whole system work. In doing so, it moves from beginner level to full fledge maturity where the working of an ecosystem is at its highest point.

Scrutinizing over the general framework of a start-up ecosystem leaves us with individual elements. An amalgamation and harmonious work of all these elements bring forth the required platform of the start-up ecosystem.

Materializing the Start-up Venture

Start-up ventures take up a central position in a start-up ecosystem. They are the core of creation, disorder, and progression. They dictate the way of a start-up ecosystem and contribute towards the overall economic growth.

As is in most ventures, the inception of a start-up begins by materializing an idea. To materialize an idea, an entrepreneur looks for required members. This creates job opportunities for the general public. Once a team has been chosen, the venture is made public to make revenue.

Start-ups have varied kinds depending upon the idea being utilized. They range from dawning ventures to well-established empires. All these different sorts have their distinctive roles to accomplish. However, the parenting phenomenon governing each of these remains the same.

Talent Hunting in Educational Institutions

It is now a fact that educational institutions and technical colleges serve as the hub for a vital public resource that is talent. High schools, universities, and technical colleges play a vital role in fostering talent and preparing a fresh crop of entrepreneurs for coming generations.

Universities offering courses on entrepreneurship, innovation, marketing, managing, and e-commerce are carving a way for young bright minds to take up entrepreneurship as their full-time occupation. In an era of rapid technological advancements, changing world order and climate threats it is now crucial for higher educational institutions to equip their students to face the multiple challenges of the new world.

Start-ups working on these challenges could be readily taken by students equipped with contemporary knowledge and thought. Moreover, for additional trials, equipping the students with technological know-how has become very important. Students could be made to join boot camps and diploma courses to fuel up their résumé for becoming a part of their local start-up ecosystem. This is what exactly @QRC Assurance and Solutions  has embarked upon.

Collaborating for Funding

Capital stands as a pivotal factor in fostering revenue. Funding providers such as investors, shareholders, loan lenders, and funding organizations act as a backbone for the working of a start-up on its way to maturity. To become successful, a start-up requires capital to be invested in not only building up the setup but also in public relations, incentives, and workspace management.

Start-ups do have special departments dedicated to money up the bank accounts for various purposes.

Substantiating with Incubators and Accelerators

Incorporating programs such as governance, mentorship, share-hold, problem-solving, and professional training comes under the vast umbrella term of incubators and accelerators. Their presence is vital for cementing an early-stage start-up of an ecosystem.

Programs such as these might provide a working space, tools, or even software development for start-ups. Joining one could give a better understanding of what goes on in the wider field. Motivational speakers, leaders, and established business tycoons could be invited for talks and seminars. Doing so widens up the prospects for potential investors and collaborators.

Co-working Spaces to the Rescue

Start-up ventures in their early stages are potentially devoid of proper working space. Due to a tight budget and meager funds, the employees often choose to work from coffee shops and specially designed co-working spaces using VPN services such as NordVPN to keep their activity secure.

Moreover, co-working spaces act as “start-up within a start-up” as it has a community of various entrepreneurs and collaborators. Freelancers, gig workers, and specialists could be found within arm’s reach.

Being in a co-working space opens up vast prospects to acquaint oneself with multiple business owners. Knowing and adopting their work ethics could prove to be highly beneficial. Moreover, co-working spaces have different employees working for different business ventures. You could get help from them if ever needed.

Others

Start-ups in their early stage have to be substantiated by various elements. Some of these elements include the assistance of agencies and consultants, service providers, mentors, tech experts, designers, event organizers, government assistance, social media, blog posts, research organizations, and corporations.

Building a Start-up Ecosystem

One of the common misconceptions regarding the inception of a start-up is that it is more or less a knock-on effect of a highly prospering economy. However, that is not always the case.

Start-ups could be seen thriving from a humble beginning and rising to the height of success. It doesn’t have to be the First World countries bagging up their banks with revenue. Chances of thriving and success are equal to all!

Countries with struggling economies and humble finances could be seen coming up with the most innovative and applicable start-up ideas.

Setting up a platform for building a start-up ecosystem has various carved steps that could be adopted for establishing your start-up. These steps are as follows:

1: Working on the Framework of a Start-up Ecosystem

It is rather crucial to set up a framework for your local ecosystem. There are various Apps on the virtual marketplace for this purpose. These Apps could be made to search for resources and frameworks of business activity in your region.

It is highly crucial to work out a scheme and a framework, to begin with. Apps such as the Start-up Ecosystem Canvas have proved to be immensely helpful and accessible.

2: Building the Community

Organizing entrepreneurial meet-up sessions, seminars, and workshops and joining a series of events could help develop engagement and work relations with other communities and entrepreneurs.

Joining virtual entrepreneurial spaces on social media assists in building a community for your venture. You could choose to involve the empires of your liking. Acquainting your team with professionals could prove to help inculcate confidence and motivation in your teammates.

3: Increasing the involvement

A good start-up ecosystem is potentially involved and connected. Entrepreneurs could involve other entrepreneurs, established businesses, and the general public by giving them incentives. You could ask the general public to devote their time to your start-up venture.

4: Becoming a Leader

Leading the crew from the front and collaborating with other ventures is the most crucial step for setting up a start-up ecosystem. Reaching out to other business communities, entrepreneurs, organizers, managers, and agencies is vital for building your start-up ecosystem.

Final Thoughts

A start-up will not take any specific number of years to become an established organization, but what it takes is, how far and deep, it has a process-orientation established, people centric policies are deployed, literally a hierarchy-less, performance oriented transparent and trustful environment is encouraged.

Finally, unless the resources working in a start-up take an ownership of their actions, even though they have been trained and deployed well, the ecosystem will not mature to make a High Impact.
PCI Secure SLC vs PCI Secure Software

The Payment Card Industry Software Security Framework, introduced by PCI SSC, is a relatively new framework that will go into effect in October 2022. The PCI SSF is a collection of various codes and tools created to safeguard payment software. It’s a framework that was created to take the position of the Payment Application Data Security Standard (PA-DSS) with more up-to-date standards that support various payment software types, technologies, and development techniques. The framework gives software developers the freedom to combine payment application security with the most up-to-date industry-best SDLC practices and frequent update cycles.
The Secure Software Lifecycle (SLC) Standard and the Secure Software Standard make up the framework. The eligibility requirements determine which standard is used. For a better understanding of the framework, the details of both standards are provided below.

What is a Secure Software Standard?

The PCI Secure Software Standard (PCI SSS) is a set of rules that Payment Software Vendors had to comply with in order to be recognized by the PCI Security Standard Council as a Validated Payment Software or Listed Payment Software. Validating the payment software guarantees that the application is developed securely and in accordance with the best practices and standards available. The validation ensures that the Payment Software was created securely to safeguard both the software’s integrity and the privacy of any sensitive data it saves, processes, or transfers.
Validation and listing are required for payment software created by the vendor that is intended to support or assist payment transactions in terms of processing, transmitting, or storing payment data, as well as software that is commercially accessible for sale to various organisations. On the PCI SSC website, there is a list of all the validated payment software that has been identified and listed.

What is the Secure Software Lifecycle standard?

A standard called the PCI Secure Software Lifecycle (SLC) was created with the aim of guaranteeing the security of the software vendor’s software development process, methodology, and practices . The ability to build secure payment software is demonstrated by comparing the organization’s software lifecycle management procedures to the Secure SLC Standard. By constructing a solid defense against attacks, this increases the assurance that the payment software is secure for supporting all types of payment transactions while also lowering risk exposure or vulnerabilities. Overall, the testing of the vendor’s SLC procedures, technology, and design, development, and maintenance of the payment software throughout the course of the whole software lifecycle establishes the level of security of the system against the PCI SLC.

Difference between PCI Secure Software Standard (SSS) and PCI Secure Software Lifecycle (SLC)

Under the Payment Software Security Framework, there are two distinct programme called Secure Software Standard (SSS) and Secure Software Lifecycle (SLC) (PCI SSF). Both curricula concentrate on various facets of software security verification. The PCI SSS evaluates the overall efficacy of the security of the programme whereas the SLC verifies the security policies and procedures used in software design and development. As a result, businesses may be verified for both the Secure Software Lifecycle for their software development process and the Secure Software Standard for any created payment software. Only software developers that create Payment Software that is sold, distributed, or licensed to third parties are subject to the PCI SSS.
This could include payment software that is installed on customers’ computers or that is intended for their use, regardless of how the programme is provided. In contrast, PCI Secure SLC is applicable to all software vendors who want to verify and guarantee the security of their Payment Software solutions. Software suppliers should be aware that if they have already been verified for SSS, they do not necessarily need to be validated against Secure SLC. Secure SLC validation, however, can make it simpler to maintain the validation of the payment programme when modifications are made to it.

PCI DSS V4.0 Core 12 Requirements – Part 2

PCI DSS 4.0 Requirement 7 –  Requirement  12 covers multiple aspects, like restriction on the cardholder data, network and user access, testing of ongoing systems and how organizations maintain their infosec policy.

Requirement 7 : Restrict Access to System Components and Cardholder Data by Business Need to Know

  • Organizations needs to establish a robust Processes and mechanisms for restricting access to system components and cardholder data by business need to know are defined and understood
  • Access to system components and data is appropriately defined and assigned
  • Access to system components and data is managed via an access control system(s).

Requirement 8 : Identify Users and Authenticate Access to System Components

  1. Organizations needs to establish a robust Processes and mechanisms for identifying users and authenticating access to system components are defined and understood
  2. User identification and related accounts for users and administrators are strictly managed throughout an account’s lifecycle
  3. Strong authentication for users and administrators is established and managed
  4. Organization must enforce multi-factor authentication (MFA) is implemented to secure access into the CDE
  5. Organization must enforce multi-factor authentication (MFA) systems are configured to prevent any misuse.
  6. Use of application and system accounts and associated authentication factors is strictly managed.

Requirement 9 : Restrict Physical Access to Cardholder Data

  1. Organizations needs to establish a robust Processes and mechanisms for restricting physical access to cardholder data are defined and understood.
  2. Physical access controls manage entry into facilities and systems containing cardholder data.
  3. Physical access for personnel and visitors is authorized and managed.
  4. Media with cardholder data is securely stored, accessed, distributed, and destroyed.
  5. Point of interaction (POI) devices are protected from tampering and unauthorized substitution

Requirement 10 : Log and Monitor All Access to System Components and Cardholder Data

  1. Organizations needs to establish a robust Processes and mechanisms for logging and monitoring all access to system components and cardholder data are defined and documented.
  2. Audit logs are implemented to support the detection of anomalies and suspicious activity, and the forensic analysis of events.
  3. Audit logs are protected from destruction and unauthorized modifications.
  4. Audit logs are reviewed to identify anomalies or suspicious activity.
  5. Audit log history is retained and available for analysis.
  6. Time-synchronization mechanisms support consistent time settings across all systems.
  7. Failures of critical security control systems are detected, reported, and responded to promptly.

Requirement 11 : Test Security of Systems and Networks Regularly

  1. Organizations needs to establish a robust Processes and mechanisms for regularly testing security of systems and networks are defined and understood.
  2. Wireless access points are identified and monitored, and unauthorized wireless access points are addressed.
  3. External and internal vulnerabilities are regularly identified, prioritized, and addressed
  4. External and internal penetration testing is regularly performed, and exploitable vulnerabilities and security weaknesses are corrected
  5. Network intrusions and unexpected file changes are detected and responded to.
  6. Unauthorized changes on payment pages are detected and responded to.

Requirement 12 : Support Information Security with Organizational Policies and Programs

A comprehensive information security policy that governs and provides direction for protection of the entity’s information assets is known.

  1. Acceptable use policies for end-user technologies are defined and implemented
  2. Risks to the cardholder data environment are formally identified, evaluated, and managed.
  3. PCI DSS compliance is managed
  4. PCI DSS scope is documented and validated
  5. Security awareness education is an ongoing activity
  6. Personnel are screened to reduce risks from insider threats
  7. Risk to information assets associated with third-party service provider (TPSP) relationships is managed
  8. Third-party service providers (TPSPs) support their customers’ PCI DSS compliance
  9. Suspected and confirmed security incidents that could impact the CDE are responded to immediately

Stay Tuned, for more information and updates on payment security !!

PCI DSS v4.0 Core 12 Requirements – Part 1

The PCI  Standards Security Council (PCI SSC) published the latest update to the PCI DSS v4.0 that has significantly shifted the focus on outcome-based. requirements. The core 12 PCI DSS requirements remained unchanged fundamentally with the revised version, however they are now realigned to significantly address how the security controls should be implemented.

PCI DSS v4.0 includes a number of changes and option to implement and validate PCI DSS requirements.

Requirement 1 : Install and Maintain Network Security Controls – Such as Firewalls and any other Network security Technologies such as VPC’s, Security Groups helps the entities to control the traffic between In/Out of their network and Internal network Segments physically or logically.

  1. Organizations needs to establish a robust Processes and mechanisms for installing and maintaining network security controls should be defined and communicate with all the stakeholders.
  2. Network security controls (NSCs) should be securely configured and maintained regularly.
  3. Network access to and from the cardholder data environment is restricted with predefined rules and policies.
  4. Network connections between trusted and untrusted networks are controlled.
  5. Risks to the CDE from computing devices that are able to connect to both untrusted networks and the CDE are mitigated.

Requirement 2 : Apply Secure Configurations to All System Components like Firewalls, Routers, Switches, Applications, Databases and any other Network security devices, End User devices etc.,

  1. Organizations needs to establish a robust Processes and mechanisms for applying secure configurations to all system components are defined and understood.
  2. System components are configured securely and managed securely.
  3. If organization using any Wireless environments, then such environments are configured and managed securely.

Requirement 3 : Protect Stored Account Data Like Card Holder Data (CHD) and Sensitive Authentication Data (CHD). Read our FAQ’s.

  1. Organizations needs to establish a robust Processes and mechanisms for protecting stored account data are defined and understood.
  2. Storage of account data is kept to a minimum as per the business and regulatory requirements.
  3. Sensitive authentication data (SAD) is not stored after authorization even if it is encrypted.
  4. Access to displays of full PAN and ability to copy cardholder data are restricted.
  5. Primary account number (PAN) is secured wherever it is stored.
  6. Cryptographic keys used to protect stored account data are secured.

Where cryptography is used to protect stored account data, key management processes and procedures covering all aspects of the key lifecycle are defined and implemented.

Requirement 4 : Protect Cardholder Data with Strong Cryptography During Transmission Over Open, Public Network.

  1. Organizations needs to establish a robust Processes and mechanisms for protecting cardholder data with strong cryptography during transmission over open, public networks are defined and documented.
  2. PAN is protected with strong cryptography during transmission.

Requirement 5 : Protect All Systems and Networks from Malicious Software like viruses, worms, Trojans, spyware, and rootkits etc.,

  1. Organizations needs to establish a robust Processes and mechanisms for protecting all systems and networks from malicious software are defined and understood.
  2. Malicious software (malware) is prevented or detected and addressed.
  3. Anti-malware mechanisms and processes are active, maintained, and monitored.
  4. Anti-phishing mechanisms protect users against phishing attacks.

Requirement 6 : Develop and Maintain Secure Systems and Software

  1. Organizations needs to establish a robust Processes and mechanisms for developing and maintaining secure systems and software are defined and understood.
  2. Bespoke and custom software are developed securely.
  3. Security vulnerabilities are identified and addressed in timely manner
  4. Public-facing web applications are protected against attacks like Man-In Middle attacks etc.,
  5. Changes to all system components are managed securely

Read about the  PCI DSS 4.0 Core 12 Requirements – Part 2, here

PIPL: China’s Own Data Security Law For PPI

China has passed the Personal Information Protection Law, referred to as the  PIPL. Currently, the Cybersecurity law protecting cybersecurity, the Data security law protecting data security, and the now the  PIPL  law protecting personal information, consisting of the data protection framework of China.

The  PIPL  will be effective from 1st November 2021, as the first comprehensive law which will remain exclusive to protect personal information. Organizations dealing with personal data related to China will have to comply with the  PIPL. Let us take a look at the highlights of the PIPL law:

PIPL Highlights : Important Definitions

  • 1. Personal Information Processor:  Article 73 defines a Personal information processor as an organization or individual that independently determines the purposes and means for the processing of personal information. “Personal information processor” in PIPL is as “Data controller” is to GDPR.
  • 2. Entrusted Party: Article 21 defines “Entrusted Party” as the entity that processes personal information.
  • 3. Personal Information: Article 4 defines Personal information as any information related to identified or identifiable natural persons recorded by electronic or other means. It is to be noted that anonymized information is not considered personal information under the PIPL.
  • 4. Processing of personal information – It is defined as the  collection, storage, use, processing, transmission, provision, publication, and erasure of personal information.

Cross border transfers

International organizations with business operations in China or Chinese organizations with international operations will have to comply with the cross-border data transfer requirements. The PIPL allows cross-border transfers. The conditions prescribed for cross border transfer are as follows:

  • 1. Article 39  states that the personal information processor must notify individuals about the transfer and obtain separate consent for it.
  • 2. Article 38  states that the personal information processor must ensure data protection measures are provided by the foreign data importer.
  • 3. Article 55  states that the personal information processor must conduct an assessment for the impact of protection of personal information.
  • 4. Article 51  states that there are multiple factors to be considered while designing data protection measures, like defining the objective and framework for processing personal information, classifying the types of information, probability of risk, and infringement of an individual’s rights and interests.

Data protection measures prescribed by the PIPL are as follows:

  • 1. Preparation of operational procedures and internal management system
  • 2. Classifying the personal information with proper classification.
  • 3. Usage of data security tools like encryption.
  • 4. Allocating clearly defined authority to process personal information.
  • 5. Providing training for the employees at regular intervals.
  • 6. Staying prepared with an emergency plan of action for security incidents.

Although the PIPL SCC has not been released, organizations can still choose to obtain a personal information protection certification or to enter into an agreement with the foreign data importer. It is evident from the cross-border data transfer requirements prescribed by the PIPL, that data security is viewed as a matter of national security.

A short review of rights under the PIPL  :-The PIPL law is majorly aligned to the requirements of the GDPR when it comes to personal information rights. Although the extent of implementation of the rights under the PIPL cannot be determined at present, the below rights of the PIPL can be compared to the rights of the GDPR :

  • 1. Right to information
  • 2. Right to access
  • 3. Right to correction or rectification
  • 4. Right to erasure
  • 5. Right to object to and restrict the processing of an individual’s data
  • 6. Right to data portability, complying with the requirements of the Cyberspace Administration of China.
  • 7. Right not to be subject to automated decision-making
  • 8. Right to withdraw consent
  • 9. Right to lodge a complaint with the regulator

A look at the penalties for non-compliance

Let us take a look at the scenario of non-compliance :

  • 1. Article 66 –  A fine of up to 50 million RMB can be issued as per Article 66. Any illegal income will be confiscated and a fine of 5% of the organization’s annual revenue(previous financial year).
  • 2. Article 67 –  Apart from the monetary fine, the violations will be recorded into “credit files” as per China’s national social credit system.
  • 3. Article 69 –  In case of infringement of rights and interests of personal information, tort damages will be levied for the organization.
  • 4. Article 70 –  In case of infringement of rights and interests of personal information of a large number of individuals, public interest lawsuits can be filed under the People’s Procuratorate.

PIPL vs GDPR

When discussing Data security laws, one more major name that arrives in the discussion is the GDPR law. Although it can be said that the PIPL has emerged drawing a few significant influences from the GDPR law, it is different from the GDPR in many ways. Let us look into a few notable differences between the  PIPL  and the GDPR law:

  • 1. Terminologies –  There are many differences in terminologies used in both laws. A few inferences are – “data subjects” in GDPR and “individuals” in PIPL, “data controllers” in GDPR and “personal information handlers” in PIPL, “data processors” in GDPR, and “entrusted parties” in  PIPL.
  • 2. Penalty –  The penalty levied by the  PIPL  is up to 5% of annual revenue. The law does not mention if the penalty is on annual revenue in China or worldwide. The penalty levied by the GDPR is 2% and 4% of annual revenue worldwide.
  • 3. Data breach notification –  In case of a data breach, the  PIPL  does not provide any deadline to issue a notification. The notification must be immediate whereas the GDPR specifies a deadline of 72 hours.
  • 4. Sensitive data –The definition of sensitive data differs between the  PIPL  and GDPR. There might be instances where the same data is classified as sensitive under the  PIPL  and not the GDPR law.

Conclusion

It is now evident that the time has arrived for companies dealing with personal information and data subjects, as China has an exclusive law for data protection. It would be the most appropriate decision to utilize this time and align the data and compliance policies of your organization in line with the PIPL. When implementing the requirements for PIPL, one must have a deep understanding of the existing requirements of the GDPR law implemented in the system.

As mentioned earlier, the PIPL has emerged drawing a few significant influences from the GDPR law. So it would be wise to go ahead with an analysis of the differences between the requirements of both these comprehensive data security laws to save time in transitioning the process differences and in avoiding penalties.

POS Device Security and the Cleanliness

POS devices and their usage have become an integral part of every customer facing business. While they provide an ease of making transaction payments, maintaining a hygiene around these crucial devices is also necessary. With  COVID-19  crisis around the clock, the risk of getting affected has quadrupled and with masses inkling more towards the user of cashless mediums to make payment, merchants are facing an increasing challenge in protecting the safety of their customers. These uncertain times requires an increased awareness about the potential risk associated with the touching the payment terminals.

The PCI SSC Council recently shared an article addressing the needs to maintain the POS hygiene and listed down some considerations to be undertaken by the merchants to maintain the security and cleanliness of the POS devices.

Prioritizing Internal Security for Hygiene

While POS devices are more customers facing, the employees handling the devices are prone as well to exposure. In such situations, access to POS devices can be reduced to specific individuals rather than the entire on-shift employees. POS vendors provide internal security feature to segment the managing staff based on multiple criteria.

Promoting Contactless Transactions

Contactless cards prove to a safe payment method for transaction, since they don’t require any physical interaction between the customer and the POS device. Owing to these many countries across the world have increased the maximum value for transactions by contactless or non-PIN means. These methods greatly reduce any physical interaction required for payment. Merchants are encouraged to contact their processor or acquirer to investigate the use of these techniques.

Hygiene of Payment Terminals

POS systems are quite an investment. The increasing pandemic further adds to the need of them to be regularly sanitized. However, many merchants use the same old methods of cleaning the devices by means of spraying disinfectants directly on the keyboard before wiping it. These leads to reduced lifespan of the electronic device.

The vendor’s instruction can come in handy at times like this since the device making varies from one vendor to another. Also, many keypads are not designed to be watertight and hence disinfectants sprayed on can damage the sensitive hardware. Keypads should be wiped gently, also in times like these, customers should be provided with a wipe and sanitizer.

POS Overlays:Precautions and Hazards

Use of Overlays has been seen as means to protect the POS devices from the spray and disinfectants. However plastic wrapping adds an additional layer of risk to the PCI PTS approved devices.

Overlays can be used to capture the card and PIN data from the ATMs and POS devices. By placing an overlay containing an illegal card reader or wires over a card, the customer data can be recorded, along with skimming or hiding of tamper evidence. Only a small degree of opaqueness is sufficient enough to slip or conceal any wire or sensor with malicious intent.

Owing to these, the use of overlays poses a securityrisk to both the merchants and consumers. The use of these on the operations device may also affect the PCI device approval. Its advisable that merchants should consult the acquirer regarding the used of overlays during these crises.

QRC’s Awareness Program

QRC has been creating awareness among the Payment Card Professionals regarding forming and putting down the best practices in use in their daily operations regularly. Being awareness of the various possible threatscape can prove to be vital for any organization is safeguarding any losses due to data breach that might lead to loss of reputation and resources.

‘Defence in Depth’ Demystified -Measures & Security Controls

Defence in Depth  (DiD) is a layering ploy, initiated by the  National Security Agency  (NSA) for facilitating an additional layer of information security. In these multiple layers of security measures are implemented within an IT infra with the ideology that if one layer of protection is in exploitation, then the additional layers would mitigate the breach risk. It is a broadened approach that is a unique combination of physical, technical, and administrative controls for security measures. It can be integrated with multiple security measures as it is a multidirectional approach and is not bound to any particular rules or regulations.

Defence in Depth is a magnified approach to set up security and privacy policies against diversified attack vectors.

Counteractive Measures of Defence in Depth :

Security Policies and Procedures- The primary outcome of setting up policies and procedures for an organization is the conservancy of confidentiality, integrity, and availability of systems and information used by organization members

  • Confidentiality involves safeguarding the assets from unauthorized individuals.
  • Integrity provides the modification of assets so that the organization is in a specified and authorized manner.
  • Availability is a state of the system in which authorized users have persistent access to specified assets.

Physical Security – A strategic approach to control physical access to the availability of sensitive information is inclusive in physical controls. Generic measures explored within this control are implementing security personnel such as guards and receptionists, installation of CCTV, automatic door access, and many more.

Perimeter Defences – It’s traditional approach for controlling traffic flowing in and out of the data centre network. Generic measures within this area are the installation of an application firewall, server firewall, and network-level firewall. Additionally, set up Intrusion Prevention System, which controls the network traffic and Intrusion Detection System for monitoring the network traffic.

Network Security – It’s an activity assigned to cushion the usability and integrity of your network(LAN, Optical Fibre, wires, WI-FI). The elemental measures within this area are as following secure your network, audit network regularly, keep O/S Patches up to date, keep Antivirus, and Malware Definitions Current, and establish Policy for Mobile and Wireless Devices.

Logging and Monitoring of Events – Logging is a standardized procedure for making a detailed set of events that occur within the application. Monitoring is analyzing the logged events to check whether the application is working in a prescribed manner. Together logging and monitoring can help you to have clarity of how your applications are working on various infrastructure components.

Logical Controls – Also termed as technical controls, they set up security measures for the software and hardware of the organization. A robust technical control measure would focus on means to identify, authenticate, authorize, or limit the authenticated user to restricted actions.

Workstation Defences – The most basic security measure is the implementation of an updated antivirus system. Other measures to go with would be keeping the application and operating system patched up and updated, assuring the workstation run in limited and administrative mode. Also, assuring that the software updates installed are from verified and genuine source.

Asset Management – Asset management permits an organization to keep a record of the asset, be it tangible or intangible in nature. In an information security environment, an asset is any data, devices, or other components that support information-related activities. Asset management helps you out to assimilate your asset inventory, asset classification, patch classification status, software package version and updates and many more.

Host Security – In layman terms, the host is a computer or any computer device which connects with the network. The purpose of host security is to prevent the host operating system, file system, and it’s resources from unauthorized access. Installation of a host-based firewall is one of the necessary preventive measures.

Session Security – Session security is a branch of information security which restraints the exposure of network when a user leaves the system neglected while still logged in. It also involves establishing several session controls to control session behavior. The standard measures within this area are standardizing default session timeout, control inactive session expiry, and sending a prompt message when the session timeout is reaching out.

Application Security – Calibration of application with certain features and functionalities to the software to prevent threats. Various application parameters must be logged and monitored periodically, encrypt the cookies and set an expiration date. While building the software the organisations should be diligent about software tampering, session tampering and cryptography.

Data Protection – Data protection approach comprises of Data lifecycle management and information life cycle management. Data lifecycle management consists of securing online and offline data storage. Information lifecycle management is a comprehensive strategy for valuing, cataloguing, and protecting information assets from application and user errors, malware, and virus attacks.

After the overall understanding of the security controls, as mentioned earlier, we can break down the formation of a secure information environment by the following described steps.

  1. Establish an Information security policy.
  2. Define and classify assets, business core components, and infrastructure.
  3. Defend at the network edge – Firewall, IDS, IPS, and Antivirus.
  4. Defend within the network edge – secure demilitarized zone, encrypt channels between each communicating devices and establish VPN connection.
  5. Defend the Internal network – implement access control measures.
  6. Defend individual system components.
  7. Train user and impart awareness among the professionals regarding best practices.
  8. Frequently test the infrastructure defences to ensure rigid security posture.
  9. Review plan and improve strategy periodically.