Understanding OSI layers from Security View – Introduction

The OSI model, or the Open Systems Interconnection model, is a conceptual framework that standardizes and describes the functions of a communication system. It was developed by the International Organization for Standardization (ISO) in the late 1970s to facilitate interoperability between different computer systems and networks. The OSI model is composed of seven distinct layers, each serving a specific purpose and responsible for a particular aspect of data communication. These layers work together to enable communication between devices and ensure that data is transmitted accurately and efficiently across a network.
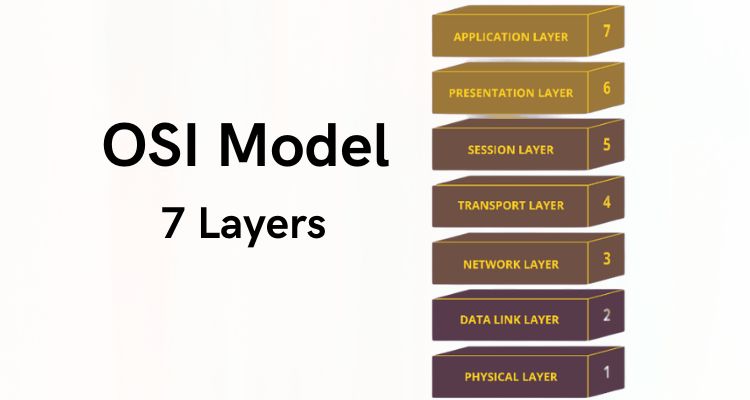


Let’s briefly explore each layer:

  1. Physical Layer: This is the lowest layer of the OSI model and deals with the physical transmission of data over a communication medium. It defines the electrical, mechanical, and physical specifications required to establish and maintain a physical link between network devices.
  2. Data Link Layer: The data link layer provides a reliable point-to-point connection for data transmission. It handles error detection and correction, as well as data framing, addressing, and flow control. Ethernet and Wi-Fi are examples of data link layer protocols.
  3. Network Layer: The network layer is responsible for the routing and forwarding of data packets across different networks. It determines the optimal path for data transmission, performs logical addressing, and handles congestion control. IP (Internet Protocol) is a widely used network layer protocol.
  4. Transport Layer: The transport layer ensures reliable and transparent end-to-end data transfer between hosts. It establishes connections, segments data into smaller units, manages flow control, and provides error recovery mechanisms. TCP (Transmission Control Protocol) and UDP (User Datagram Protocol) are common transport layer protocols.
  5. Session Layer: The session layer establishes, maintains, and terminates connections between applications on different network devices. It enables synchronization, checkpointing, and recovery of communication sessions.
  6. Presentation Layer: The presentation layer is responsible for data representation, encryption, compression, and formatting. It ensures that data from the application layer is properly formatted and compatible with the receiving device.
  7. Application Layer: The application layer is the topmost layer and interacts directly with end-user applications. It provides network services and supports protocols for specific applications, such as HTTP (Hypertext Transfer Protocol) for web browsing and SMTP (Simple Mail Transfer Protocol) for email.

By dividing the network communication process into these seven layers, the OSI model allows for modular design, easier troubleshooting, and the ability to replace or upgrade individual layers without affecting the entire system.

Understanding the OSI model and its layers is crucial for network administrators, engineers, and anyone involved in designing, implementing, or troubleshooting computer networks. It provides a common reference point for communication protocols and helps ensure interoperability in complex network environments.
Enhancing Security: PAN Removal and Secure Hashing – II

III. Keyed Cryptographic Hashing Algorithms :

To augment the security of hashed PANs, organizations can employ keyed cryptographic hashing algorithms. These algorithms incorporate a randomly generated secret key into the hashing process, significantly enhancing data protection against brute force attacks and ensuring secret authentication integrity.

HMAC (Hash-based Message Authentication Code):

HMAC is a widely used keyed cryptographic hashing algorithm that combines cryptographic hash functions with a secret key. It provides a robust mechanism to verify the integrity and authenticity of data. HMAC employs a specific hash function, such as SHA-256, along with a secret key, to generate a unique hash value for each PAN.

The process of computing an HMAC involves the following steps:

  1. a) Message Padding:The PAN is padded to ensure a consistent length, as required by the hash function.
  2. b) Key Padding:The secret key is also padded to match the block size of the underlying hash function.
  3. c) Inner Hash:The padded secret key is XORed with a predefined inner padding value, and the result is concatenated with the padded PAN. The concatenated data is then hashed using the chosen hash function.
  4. d) Outer Hash:The hashed result from the inner hash step is concatenated with the padded secret key XORed with a predefined outer padding value. The combined data is hashed again using the chosen hash function.

The final output of the HMAC process is the unique hash value that represents the PAN’s integrity and authenticity. Verifying the integrity of a PAN involves re-computing the HMAC using the stored secret key and comparing the generated hash value with the stored hash value.

CMAC (Cipher-based Message Authentication Code):

CMAC is another keyed cryptographic hashing algorithm that provides enhanced security by preventing known-plaintext attacks. It is based on a block cipher, such as AES (Advanced Encryption Standard), and employs a secret key to generate a message authentication code.

The process of computing a CMAC involves the following steps:

  1. a) Initialization:The CMAC algorithm initializes the block cipher with the secret key, setting up the initial state.
  2. b) Message Processing:The PAN is processed block by block using the block cipher’s encryption function, incorporating the secret key and the previous block’s result.
  3. c) Padding:If the PAN length is not a multiple of the block size, padding is applied to ensure a complete block.
  4. d) Finalization:The final block is processed using the block cipher, producing the CMAC value.

Similar to HMAC, verifying the integrity of a PAN using CMAC involves re-computing the CMAC value and comparing it to the stored value.

GMAC (Galois Message Authentication Code):

GMAC is a keyed cryptographic hashing algorithm primarily used in authenticated encryption schemes, providing both confidentiality and integrity assurances. It employs a secret key, a nonce (a unique number used once), and a message to generate a MAC (Message Authentication Code) that guarantees data integrity and authenticity.

The process of computing a GMAC involves the following steps:

  1. a) Initialization:The GMAC algorithm initializes the Galois field, incorporating the secret key.
  2. b) Message Processing:The PAN, along with the nonce, is processed block by block using the Galois field multiplication and addition operations.
  3. c) Finalization:The final GMAC value is generated by processing the last block and incorporating the final Galois field calculations.

GMAC enables the recipient of the PAN to validate the integrity and authenticity of the data by re-computing the GMAC value using the received PAN, the same secret key, and the nonce.

Conclusion:

In an era where data breaches and unauthorized access pose significant threats to organizations and their customers, implementing robust data security measures is crucial. Cleartext PAN removal serves as a critical defense-in-depth control, ensuring that stored PANs remain protected even in the event of an unauthorized breach. By encrypting or hashing PANs, organizations mitigate the risk of exposing sensitive data to unauthorized individuals.

Furthermore, secondary independent control systems, including cryptographic key management and governance frameworks, bolster the overall security posture. These systems ensure that access to cryptographic and decryption keys is tightly controlled, reducing the likelihood of unauthorized access and misuse.

Keyed cryptographic hashing algorithms, such as HMAC, CMAC, and GMAC, provide an additional layer of security by incorporating randomly generated secret keys. These algorithms resist brute force attacks and enhance the integrity and authenticity of hashed PANs.

By adopting these practices, organizations demonstrate a commitment to data security, safeguarding sensitive information and maintaining the trust of their customers and stakeholders. It is imperative to continually reassess and update data security measures to stay ahead of evolving threats and ensure the long-term protection of valuable data assets.

Tech Advancements: Essential Skills for AI-Era Security Testers

In today’s rapidly evolving technological landscape, security testers and penetration testers play a critical role in safeguarding organizations against cyber threats. As technology advances, professionals in this field must adapt and acquire new skills to effectively leverage the latest tools and methodologies. This blog post explores essential skills for security testers to stay relevant and thrive in an era driven by artificial intelligence (AI) and automation.

OpenAI, as an artificial intelligence organization, does not directly take jobs or replace professionals such as security testers or penetration testers. OpenAI’s primary focus is on developing advanced AI models like BurpGPT, PentestGPT which can assist users in generating human-like text and providing information.

It is important to recognize that AI is often viewed as a tool that can complement and assist human professionals rather than replace them. AI can help security testers by increasing efficiency, providing insights, and identifying potential vulnerabilities. However, human expertise is still crucial for contextual understanding, making judgment calls, and dealing with complex or novel situations.

Stay current: Acquire vital skills for tech-driven security testing

  1. AI and Machine Learning:  Understanding AI and machine learning concepts empowers security testers to harness the potential of AI-driven tools and technologies. Familiarity with machine learning algorithms, data analysis, and model training enables professionals to effectively utilize AI-based security solutions and identify potential vulnerabilities.
  2. Automation and Scripting:  Automation and scripting skills can significantly enhance productivity and efficiency in security testing. Proficiency in programming languages such as Python or PowerShell allows professionals to automate repetitive tasks, create customized testing scripts, and perform data analysis, freeing up time for more critical security assessments.
  3. Cloud Security:  As organizations increasingly adopt cloud-based infrastructures, security testers must acquire knowledge of cloud security concepts, platforms (e.g., AWS, Azure), and best practices. Understanding cloud-specific security controls, identity and access management, and data protection is crucial for securing cloud environments effectively.
  4. DevOps and Continuous Integration/Continuous Deployment (CI/CD):  DevOps practices are now commonplace, and security testers should familiarize themselves with DevOps principles and methodologies. This includes understanding CI/CD pipelines, containerization technologies (e.g., Docker), and integrating security practices into the development lifecycle to ensure secure and resilient applications.
  5. Secure Coding and Secure Development Lifecycle (SDL):  Proficiency in secure coding practices and the SDL is essential for security testers. Understanding common vulnerabilities (e.g., OWASP Top 10), secure coding standards, and performing code reviews allows professionals to identify potential weaknesses in software applications and ensure secure development practices are followed.
  6. Threat Intelligence:  Staying updated on the latest threat landscape and emerging attack techniques is critical for security testers. Continuous research on current cyber threats, novel vulnerabilities, and evolving attack vectors allows professionals to effectively assess and mitigate risks during security testing and penetration testing engagements.
  7. Communication and Collaboration:  Effective communication and collaboration skills are invaluable for security testers. Being able to articulate technical concepts, collaborate with development teams, and convey security findings to non-technical stakeholders ensures that security assessments are well-understood and actionable by all involved parties.

To learn the new skills mentioned above, here are some effective ways you can consider:

  • Online Courses and Tutorials: Platforms like Coursera, Udemy, and edX offer a wide range of online courses covering AI, machine learning, cloud security, programming languages, and more. These courses provide structured learning paths, practical exercises, and certifications.
  • Open Source Projects and Communities: Engaging with open source projects on platforms like GitHub allows professionals to contribute, gain hands-on experience, and collaborate with experienced individuals in the field.
  • Books and Documentation: Utilize authoritative books and technical documentation to delve deep into the topics of interest. These resources provide in-depth knowledge, practical examples, and guidance from experts.
  • Practical Projects and Challenges: Building practical projects and participating in coding challenges solidify understanding and enhance skills. Real-world applications and security-related challenges sharpen expertise and provide valuable experience.
  • Virtual Labs and Hands-On Practice: Utilize virtual labs and online platforms that offer hands-on practice environments for security testing, programming, or cloud platforms. These platforms allow professionals to experiment with tools and technologies without impacting real systems.
  • Professional Certifications: Industry-recognized certifications like CEH, OSCP, or cloud-specific certifications validate knowledge and demonstrate expertise. These certifications add credibility and showcase proficiency to potential employers.

Conclusion:  In the ever-evolving field of security testing, acquiring new skills is essential for professionals to adapt to technological advancements. AI, automation, cloud security, and DevOps practices are transforming the landscape, demanding that security testers equip themselves with relevant expertise. By embracing continuous learning, engaging with communities, and staying updated with industry trends, professionals can ensure their skills remain relevant, bolstering their position in an era driven by AI and automation.

PCI DSS Network Segmentation: Explained

Network segmentation is the practice of dividing a computer network into smaller, isolated segments or subnetworks. Each segment is created to have its own distinct set of security controls and access rules, providing separation and isolation between different groups of devices, systems, or users.

The primary purpose of network segmentation is to enhance network security by reducing the attack surface and limiting the potential impact of a security breach. By segmenting a network, organizations can create barriers and control points that restrict unauthorized access and lateral movement within the network.

Network segmentation can be implemented in various ways, including:

  1. Physical Segmentation: Physically separating different network segments using separate switches, routers, or network cables. This creates a physical barrier between segments, making it harder for an attacker to move from one segment to another.
  2. VLAN Segmentation: Utilizing virtual LAN (VLAN) technology to logically separate network segments within a shared physical infrastructure. VLANs allow different groups of devices or systems to be isolated and communicate only with authorized segments.
  3. Subnet Segmentation: Dividing a network into multiple subnets, where each subnet represents a separate segment. This is typically achieved through IP addressing and subnet masks, which determine the range of IP addresses assigned to each segment.
  4. Firewall Segmentation: Implementing firewalls to enforce access controls and policies between network segments. Firewalls can filter and inspect network traffic, allowing or blocking communication based on predefined rules.
  5. Software-Defined Networking (SDN): Using SDN technologies to dynamically define and manage network segments. SDN enables flexible and programmable network segmentation based on software-defined policies and virtualized network functions.

The specific segmentation approach and techniques employed will vary depending on the organization’s network architecture, security requirements, and regulatory compliance needs.

Overall, network segmentation provides a layered defense strategy by separating and isolating critical assets, sensitive data, and different user groups. It improves network security, reduces the risk of unauthorized access, enhances monitoring and control capabilities, and helps organizations better protect their valuable information assets.

Why network segmentation is very crucial for Compliance to  PCI DSS ?

If the organization opted for Network Segmentation what is the advantages and if not what is the disadvantages for the organization while implementing PCI DSS

Network segmentation is crucial for compliance with PCI DSS because it helps reduce the scope of the cardholder data environment (CDE). By segmenting the network, an organization can isolate the systems that handle cardholder data from the rest of the network, limiting the exposure of sensitive information and reducing the potential impact of a security breach.

Advantages of network segmentation for PCI DSS compliance include:

  1. Reduced Scope: Segmentation allows the organization to limit the systems and network segments that fall within the scope of PCI DSS compliance. This simplifies the compliance process, reduces costs, and minimizes the risks associated with a broader network environment.
  2. Enhanced Security: Segmentation creates barriers and controls between different network segments, making it more difficult for an attacker to move laterally within the network. It helps prevent unauthorized access to cardholder data by isolating sensitive systems.
  3. Improved Monitoring and Control: With network segmentation, it becomes easier to monitor and control network traffic, identify anomalies, and detect potential security incidents. This enables quicker response times and more effective incident management.

Disadvantages of not implementing network segmentation for PCI DSS compliance include:

  1. Increased Risk: Without network segmentation, the entire network becomes part of the cardholder data environment, which significantly increases the risk of unauthorized access to sensitive data. A breach in one area of the network can potentially compromise the entire network.
  2. Complex Compliance: PCI DSS compliance becomes more challenging when the entire network is in scope. The organization must implement security controls and measures across a larger surface area, making compliance management more complex and resource-intensive.
  3. Higher Costs: The broader scope of compliance requires additional resources, including security tools, monitoring systems, and ongoing maintenance. The costs associated with securing and maintaining a larger network environment can be higher compared to a segmented network.

In summary, network segmentation provides significant advantages for PCI DSS compliance, including reduced scope, enhanced security, and improved monitoring. Not implementing network segmentation increases the risk of data breaches, complicates compliance efforts, and can lead to higher costs for the organization.

Is it mandatory to have Network Segmentation as per the PCI Standards ?

The Payment Card Industry Data Security Standard (PCI DSS) does not mandate specific network segmentation requirements because it is designed to be a flexible and scalable standard applicable to a wide range of organizations. The PCI Security Standards Council recognizes that different organizations have varying network architectures, infrastructures, and security needs.

While network segmentation is highly recommended as a best practice for securing cardholder data, the PCI DSS does not prescribe a one-size-fits-all approach. Instead, it provides a set of security requirements that organizations must meet to protect cardholder data, regardless of their chosen network architecture.

The flexibility allows organizations to assess their unique circumstances and determine the most appropriate methods for securing their networks. This includes evaluating the benefits and risks associated with network segmentation and deciding whether to implement it based on their specific environment, risk profile, and compliance objectives.

However, it’s important to note that even though network segmentation is not mandated, it is widely recognized as an effective security control and is strongly recommended by industry experts to enhance the security of cardholder data. Organizations are encouraged to consider network segmentation as a proactive measure to reduce the scope and impact of security breaches and improve their overall security posture.

Here are some recommended practices to consider when implementing network segmentation:

  • Identify Data Flows: Understand the flow of sensitive data within your organization. Identify the systems, applications, and network components that handle or have access to cardholder data. This will help you determine the appropriate network segments and boundaries.
  • Create Segmentation Zones: Divide your network into logical segments or zones based on the sensitivity of the data and the access requirements. Common segmentation zones include the cardholder data environment (CDE), internal networks, DMZ (Demilitarized Zone), and guest/public networks.
  • Implement Access Controls: Enforce strict access controls between network segments using firewalls, routers, VLANs, or other network security devices. Configure these devices to allow only necessary and authorized communication between segments, while blocking or limiting traffic from untrusted sources.
  • Separate Cardholder Data: Isolate systems that handle cardholder data from other non-payment systems. This can be achieved through physical or logical separation, ensuring that only authorized personnel have access to the cardholder data environment.
  • Monitor and Log Network Traffic: Deploy network monitoring and logging solutions to capture and analyze network traffic between segments. This enables timely detection of any unauthorized or suspicious activities, helping to identify and respond to potential security incidents.
  • Regularly Update and Patch Systems: Keep all network components and systems within each segment up to date with the latest security patches and updates. Regularly apply security patches to mitigate vulnerabilities that could be exploited to bypass segmentation controls.
  • Segment Wireless Networks: If your organization uses wireless networks, implement separate wireless segments for guest/public access and internal use. Apply appropriate security measures such as encryption, strong authentication, and network segregation to protect sensitive data.
  • Test and Validate Segmentation: Regularly conduct penetration testing and vulnerability assessments to validate the effectiveness of your network segmentation. Identify any gaps or vulnerabilities and address them promptly to ensure the segmentation controls remain robust.
  • Document and Maintain Segmentation: Maintain up-to-date documentation that clearly defines the network segmentation strategy, including the purpose of each segment, the allowed communication paths, and the associated security controls. Regularly review and update the documentation as network changes occur.
  • Periodically Review Segmentation: Conduct periodic reviews of the network segmentation implementation to ensure it aligns with the evolving security needs of your organization. Adjust and fine-tune segmentation controls as necessary to adapt to changes in technology, business requirements, and emerging threats.

How to check the Effectiveness of Network Segmentation ?

  • Review Network Architecture: Begin by reviewing the organization’s network architecture diagrams and documentation. This will provide an overview of the network segmentation strategy and help you understand the intended boundaries and isolation between network segments.
  • Network Scanning and Enumeration: Perform network scanning and enumeration to identify active hosts and network segments. Use tools like Nmap or Nessus to identify IP ranges, subnets, and the presence of any interconnected systems that should be isolated.
  • Traffic Analysis: Analyze network traffic to determine if there is any unauthorized or unexpected communication between different network segments. Use network monitoring tools like Wireshark or Suricata to capture and analyze network packets for any anomalies or violations of the intended segmentation.
  • Access Control Verification: Evaluate access control mechanisms, such as firewalls, routers, or VLAN configurations, to ensure they are properly configured to enforce the intended segmentation boundaries. Check for any misconfigurations or rules that allow unauthorized traffic between segments.
  • Penetration Testing: Conduct penetration testing to simulate attacks and attempts to bypass network segmentation controls. Testers should attempt to access sensitive systems or data from unauthorized network segments and assess the effectiveness of the segmentation controls in place.
  • Vulnerability Assessment: Perform vulnerability scanning and assessment to identify any potential weaknesses or vulnerabilities in the network segmentation implementation. Look for vulnerabilities that could allow unauthorized access or compromise the segmentation controls.
  • Review Policies and Procedures: Evaluate the organization’s policies and procedures related to network segmentation. Check if there are clear guidelines and controls in place for network segmentation, including change management processes, access control policies, and regular reviews or audits of segmentation configurations.
  • Interviews and Documentation Review: Interview relevant personnel responsible for network architecture, security, and operations. Review documentation, such as network segmentation plans, configuration guides, and change management records, to ensure that network segmentation is consistently applied and maintained.

By performing these testing activities, you can gain insights into the effectiveness and adequacy of the network segmentation controls implemented by the organization and identify any areas that require improvement or remediation to align with the intended segmentation objectives.

PCI Compliance: Securing Payments – Essential Guide

In the world of payment card transactions, maintaining PCI DSS compliance is crucial for businesses. Regular PCI compliance checks play a vital role in ensuring a secure payment environment. In this comprehensive guide, we will explore the importance of PCI DSS compliance checks, the key requirements, and best practices to help your organization meet and maintain compliance. By understanding the process of PCI compliance checks, you can protect cardholder data, mitigate risks, and safeguard your reputation.

Understanding PCI DSS Compliance

PCI DSS (Payment Card Industry Data Security Standard) provides a baseline of technical and operational requirements designed to protect account data. It applies to any organization that processes, stores, or transmits cardholder data. Compliance demonstrates a commitment to maintaining a secure payment environment and helps prevent data breaches and financial losses.

The Importance of Regular Compliance Checks

Regular PCI compliance checks offer several benefits, including:

  • Security Assurance: Ensuring ongoing adherence to PCI DSS requirements and maintaining a robust security posture.
  • Risk Mitigation: Identifying and addressing potential vulnerabilities and gaps before they are exploited by attackers.
  • Compliance Validation: Demonstrating to customers and stakeholders that you prioritize security and adhere to industry standards.
  • Financial Protection: Avoiding costly penalties, fines, and reputational damage associated with non-compliance.

PCI DSS Compliance Requirements

PCI DSS consists of twelve main requirements that organizations must meet. These include:

Conducting a PCI Compliance Checks

To perform a PCI compliance check effectively, follow these steps:

  1. Review Requirements: Familiarize yourself with the specific PCI DSS requirements relevant to your organization.
  2. Assess Security Controls: Evaluate your current security controls and practices against the PCI DSS requirements.
  3. Identify Non-Compliance: Identify areas of non-compliance or potential vulnerabilities that need to be addressed.
  4. Document Findings: Document the findings and recommendations for future reference and remediation planning.

Tools and Resources for PCI Compliance Checks

Several tools and resources can assist with PCI compliance checks:

  • PCI Scanning Tools: Use automated vulnerability scanning tools to identify and assess potential vulnerabilities.
  • Self-Assessment Questionnaires (SAQs): Merchants can use SAQs to self-assess their compliance based on their specific payment processing methods.
  • Qualified Security Assessors (QSAs): Engage QSAs for external audits and expert assessments to validate compliance.

Addressing Non-Compliance and Remediation

Addressing non-compliance is critical for maintaining a secure payment environment. Take the following steps for remediation:

  1. Develop a Remediation Plan: Create a comprehensive plan to address identified non-compliance issues.
  2. Implement Security Controls: Apply necessary security patches, updates, and configurations to strengthen controls.
  3. Enhance Security Practices: Enhance access controls, encryption mechanisms, and employee awareness programs.
  4. Rechecks and Validations: Conduct rechecks and validations to ensure that the remediation efforts have effectively addressed the non-compliance issues.

Best Practices for PCI Compliance Checks

Follow these best practices to ensure effective PCI compliance checks:

  • Regular Reviews: Conduct regular internal assessments and audits to maintain compliance.
  • Educate Employees: Educate and train employees on security awareness and compliance practices.
  • Implement Strong Controls: Establish and enforce strong access controls, encryption, and secure configurations.
  • Engage Experts: Seek guidance from third-party experts, such as QSAs, for independent assessments and audits.

Staying Ahead of PCI Compliance

To stay ahead of PCI compliance requirements:

  1. Stay Informed: Stay updated on changes and updates to the PCI DSS standards.
  2. Continuous Monitoring: Implement continuous security monitoring and testing to identify new vulnerabilities promptly.
  3. Embrace Emerging Technologies: Adopt emerging security technologies and practices to strengthen your security posture.

PCI compliance checks are essential for organizations that handle payment card transactions. By conducting regular checks, addressing non-compliance, and implementing strong security controls, you can protect cardholder data, minimize risks, and maintain a secure payment environment. Prioritize PCI DSS compliance checks as an integral part of your security strategy and safeguard your business from potential threats and vulnerabilities.

PCI DSS Gap Assessment: Enhancing Compliance & Security

In today’s digital world, where payment card data is constantly at risk, organizations must prioritize the security of their systems and ensure compliance with industry standards. A PCI DSS gap assessment plays a vital role in identifying vulnerabilities and bridging the gaps to safeguard sensitive cardholder data. In this blog, we will explore the key elements of gap assessment, the process involved, and the benefits of conducting a gap assessment.

Understanding PCI DSS Gap Assessment:

PCI DSS is a set of security standards established by major payment card brands to protect cardholder data and maintain a secure payment environment. While compliance refers to meeting the standard’s requirements, a gap assessment helps identify areas where an organization falls short. By conducting a gap assessment, businesses can proactively address vulnerabilities, mitigate risks, and ensure the confidentiality, integrity, and availability of cardholder data.

Scope and Applicability:

PCI DSS applies to organizations of all sizes that process, store, or transmit payment card data. The standard consists of four compliance levels, determined by the annual transaction volume. Each level has specific requirements that organizations must meet. Understanding the scope and applicability of PCI DSS is crucial in determining the extent of the gap assessment and compliance efforts needed.

PCI Data Security Standard v4.0 – High Level Overview

Key Elements of a Gap Assessment:

  1. Data discovery and classification: Identify where payment card data resides within the organization and classify it based on sensitivity. This step lays the foundation for implementing appropriate security controls.
  2. Network segmentation: Divide the network into secure segments to isolate cardholder data from other systems, minimizing the potential impact of a security breach.
  3. Vulnerability assessment: Conduct regular scans and assessments to identify weaknesses and vulnerabilities in the system infrastructure. Address these vulnerabilities promptly to prevent exploitation.
  4. Penetration testing: Simulate real-world attacks to identify potential entry points and assess the effectiveness of existing security measures. Penetration testing helps uncover vulnerabilities that automated scans may miss.
  5. Security policy and procedure review: Evaluate existing security policies and procedures against the PCI DSS requirements. Identify any gaps and make necessary revisions to align with the standard.
  6. Incident response planning: Establish an incident response plan to effectively respond to security incidents and data breaches. A well-defined plan helps minimize the impact of an incident and facilitates timely resolution.

Conducting a PCI DSS Gap Assessment:

  1. Preparing for the assessment: Understand the scope, objectives, and compliance requirements. Establish a project team, define responsibilities, and gather necessary documentation.
  2. Gathering necessary documentation: Collect relevant policies, procedures, network diagrams, system configurations, and other documentation required for the assessment.
  3. Performing technical assessments: Conduct data discovery, network segmentation analysis, vulnerability assessments, and penetration testing. Utilize appropriate tools and techniques to identify potential security gaps.
  4. Analyzing the findings: Thoroughly analyze the assessment results, identifying gaps and areas of non-compliance. Prioritize the gaps based on risk severity.
  5. Documenting the gaps and recommendations: Document the identified gaps and provide clear recommendations for remediation. Include specific actions to address each gap, ensuring alignment with PCI DSS requirements.
  6. Developing a remediation plan: Create a comprehensive plan that outlines the necessary steps, timelines, and responsible parties for addressing the identified gaps. Prioritize remediation efforts based on risk and resource availability.
  7. Addressing Identified Gaps: To bridge the gaps identified during the assessment, organizations should:
  8. Implement necessary security controls: Deploy and configure appropriate security controls to address the identified vulnerabilities and gaps.
  9. Enhance network and system security: Regularly update software and systems, patch vulnerabilities, strengthen access controls, and encrypt sensitive data to enhance overall security.
  10. Improve policies and procedures: Revise and update security policies, procedures, and guidelines to align with PCI DSS requirements. Train employees to ensure awareness and adherence to the updated policies.

PCI DSS Gap Assessment Benefits:

Apart from ensuring compliance with industry standards, a PCI DSS gap assessment offers several significant benefits to organizations,

Provides a comprehensive understanding of an organization’s current security posture:  By identifying vulnerabilities and gaps in security controls, the assessment enables businesses to prioritize their efforts and allocate resources effectively to address the most critical areas of concern. This proactive approach helps prevent security breaches, protect sensitive cardholder data, and safeguard the organization’s reputation.

Secondly, a PCI DSS gap assessment helps organizations enhance their overall security posture. By implementing the recommended remediation actions, organizations can strengthen their security controls, systems, and processes. This not only improves their ability to comply with PCI DSS requirements but also strengthens their resilience against evolving cyber threats and attacks. The assessment acts as a roadmap for implementing robust security measures, leading to enhanced data protection and reduced risks of financial loss and reputational damage.

A successful PCI DSS gap assessment demonstrates an organization’s commitment to security and compliance. It instills confidence in customers, partners, and stakeholders, as they can trust that their payment card data is handled responsibly. Compliance with PCI DSS not only meets the requirements set by payment card brands but also aligns with broader data protection and privacy regulations. This alignment can simplify compliance efforts for organizations operating in multiple regulatory environments.

IRDAI Issues Revised Information and Cyber Security Guidelines’23

The Insurance Regulatory and Development Authority of India (IRDAI) recently issued revised Information and Cyber Security Guidelines “IRDAI Information and Cyber Security Guidelines” on 24th April 2023.These guidelines refer to the wide-spread adoption of digital technologies and the concurrent increase in cyber security incidents. The revised guidelines are aimed at enabling the insurance industry to strengthen their defenses as well as related governance mechanisms to deal with such emerging cyber threats.

It indicates that all Insurers including FRBs, Insurance Intermediaries covering Brokers, Corporate Agents, Web Aggregators, TPAs, IMFs, Insurance Repositories, ISNP, Corporate Surveyors, MISPs, CSCs and Insurance Information Bureau of India (IIB) shall adhere to these guidelines. Those entities who have already completed the security audit for FY 2022-23 shall ensure compliance with these guidelines from next financial year.

Read the Complete Guideline here : IRDA Information and Cyber Security Guideline 2023

The IRDAI has taken a proactive step in issuing these revised guidelines to ensure that the insurance industry is well-equipped to deal with the increasing threat of cyber-attacks. It is important for all entities in the insurance industry to adhere to these guidelines and take necessary measures to protect themselves and their customers from cyber threats.

Key Highlights of IRDAI Information and Cyber Security Guidelines, 2023

  • The new guidelines are aimed at improving the cybersecurity practices of insurance companies and intermediaries
  • Primary objective of the guidelines is to bolster the industry’s defenses against cyber threats and enhance its governance mechanisms.
  • Insurers and intermediaries are mandated to deploy suitable security controls, prepare incident response plans, and conduct frequent security audits. The guidelines stress the significance of adopting a risk-based approach to information and cyber security.
  • Entities that have undergone a security audit for the fiscal year 2022-23 must ensure that they comply with the guidelines from the upcoming financial year.

One of the guidelines states that third-party entities are allowed to access an insurance company’s internal systems solely for viewing purposes. This includes accessing data, proposals, and reports, but not uploading or editing any information. They are only permitted to view products, proposals, documents, and reports. Another guideline specifies that entities that store an insurer’s non-public data, including policyholder and investment information, should not have authorization to access the insurer’s systems for the purpose of editing or maintaining such data.

By adhering to these guidelines, companies can ensure that they are taking all necessary steps to protect themselves and their customers from cyber-attacks. This includes implementing strong security measures such as firewalls and encryption, regularly updating software and systems, and training employees on cyber security best practices.

To ensure the security and confidentiality of sensitive data and to mitigate potential cyber threats, all insurance companies and intermediaries must adhere to these guidelines. If an entity has already undergone a security audit for the fiscal year 2022-23, they are obligated to comply with these guidelines starting from the following financial year.

According to recent statistics, among the 829 million cyber-attacks detected and blocked globally by a firm in the fourth quarter of 2022, close to 59 per cent were directed towards India.

As Stephane Nappo said: “Cyber-Security is much more than a matter of IT. It is essential for all entities in the industry to take necessary measures to protect themselves and their customers from cyber threats.

In today’s digital age, cyber security is a major concern for all industries, including the insurance industry. With the increasing use of digital technologies and the growing threat of cyber-attacks, it is essential for companies to have robust cyber security measures in place.  The IRDAI’s revised Information and Cyber Security Guidelines provide a framework for companies in the insurance industry to strengthen their defenses against cyber threats. It is essential for all entities in the industry to adhere to these guidelines and take necessary measures to protect themselves and their customers from cyber threats.

Understanding Vulnerability Assessment

In today’s digital landscape, organizations face a constant threat of cyberattacks and data breaches. To effectively protect sensitive information, it’s crucial to conduct regular vulnerability assessments. This blog will delve into the world of vulnerability assessments, explaining their significance in cybersecurity and providing insights into best practices. By understanding vulnerability assessments, you can proactively identify and address potential security weaknesses, safeguarding your organization’s valuable assets.

What is a Vulnerability Assessment ?

Let’s start with “what does Vulnerability mean? It is the inability to resist a hazard or to respond when a disaster has occurred. For instance, people who live on plains are more vulnerable to floods than people who live higher up.  A vulnerability in cyber security refers to any weakness in an information system, system processes, or internal controls of an organization. These vulnerabilities are targets for lurking cybercrimes and are open to exploitation through the points of vulnerability.  A vulnerability assessment is a systematic approach to identify, quantify, and prioritize security vulnerabilities within an organization’s systems, networks, and applications. It involves assessing various types of vulnerabilities, such as software flaws, configuration weaknesses, network vulnerabilities, and human factor vulnerabilities. By conducting vulnerability assessments, organizations gain a comprehensive understanding of their security posture and can take proactive measures to mitigate risks.

The Importance of Vulnerability Assessments

Vulnerability assessments offer numerous benefits to organizations, including:

  • Risk Identification: They help identify potential vulnerabilities and weaknesses that could be exploited by malicious actors.
  • Prioritized Remediation: By assessing the severity and impact of vulnerabilities, organizations can prioritize their remediation efforts, focusing on critical weaknesses that pose the highest risk.
  • Compliance Requirements: Vulnerability assessments play a vital role in meeting regulatory compliance requirements, as many industry standards and regulations necessitate regular security assessments.
  • Cost Savings: Proactively addressing vulnerabilities through assessments can save organizations from costly security breaches, financial losses, and reputation damage.

The Vulnerability Assessment Process

  1. Planning and Scoping: Define the scope and objectives of the assessment, including the systems, networks, and applications to be assessed.
  2. Information Gathering: Collect necessary information about the target environment, such as network diagrams, system configurations, and asset inventories.
  3. Vulnerability Identification: Utilize specialized tools to scan and detect vulnerabilities within the target systems, networks, and applications.
  4. Assessment and Prioritization: Analyze the identified vulnerabilities, assess their severity and potential impact, and prioritize them based on risk levels.
  5. Remediation and Mitigation: Develop a remediation plan to address the identified vulnerabilities, implementing appropriate security controls and fixes.
  6. Validation and Reporting: Validate the effectiveness of remediation efforts and prepare comprehensive reports outlining the findings, recommendations, and ongoing risk management strategies.

Tools and Techniques for Vulnerability Assessment

Several tools and techniques aid in vulnerability assessments:

  1. Vulnerability Scanners: Automated tools that scan networks and systems, identifying known vulnerabilities and misconfigurations.
  2. Penetration Testing: Simulating real-world attacks to identify vulnerabilities that automated scans might miss..
  3. Security Configuration Reviews: Assessing system configurations against industry best practices to identify weaknesses.
  4. Source Code Analysis: Examining application source code to identify vulnerabilities within the codebase.

Best Practices for Effective Vulnerability Assessments

To ensure successful vulnerability assessments, follow these best practices:

  • Conduct assessments regularly and systematically to maintain an up-to-date understanding of your security posture.
  • Keep vulnerability databases and scanning tools up to date to detect the latest vulnerabilities.
  • Prioritize critical vulnerabilities based on their potential impact and likelihood of exploitation.
  • Foster collaboration among stakeholders, including IT teams, management, and third-party experts.
  • Document findings, recommendations, and remediation efforts for future reference and compliance purposes.

Integrating Vulnerability Assessments into Your Security Strategy

Vulnerability assessments should be an integral part of an organization’s broader security strategy. By integrating the findings from vulnerability assessments with incident response plans, risk management frameworks, and security controls, organizations can

ensure a holistic approach to cybersecurity.

Future Trends in Vulnerability Assessment

The field of vulnerability assessment is continuously evolving. Keep an eye on these emerging trends:

  • Artificial Intelligence and Machine Learning: These technologies are being leveraged to enhance vulnerability detection and automate assessment processes.
  • Cloud-based Vulnerability Assessment Solutions: Cloud platforms offer scalable and centralized vulnerability assessment tools and services.
  • Automation and Orchestration: The automation of vulnerability assessments and their integration with security operations streamline processes, saving time and effort.

Vulnerability assessments are crucial for identifying and mitigating security risks. By implementing regular assessments, organizations can proactively address vulnerabilities, minimize the likelihood of successful attacks, and protect their valuable assets. Embrace vulnerability assessments as a fundamental component of your cybersecurity strategy, and you’ll be better equipped to face the evolving landscape of cyber threats.

Compliance Beyond Regulation: Business Benefits in the Long Run

Compliance goes beyond simply adhering to regulations it’s about creating a culture of ethical behavior and responsibility. By prioritizing compliance, businesses can prevent costly fines and reputational damage while building trust with their stakeholders. But compliance shouldn’t just be seen as a necessary evil. In fact, embracing compliance beyond regulation can bring long-term benefits to a business, such as improved operational efficiency, increased customer loyalty, and a stronger reputation in the market. Prioritizing compliance would help, businesses position themselves for success both now and in the future. 

In today’s business landscape, regulatory compliance is more important than ever before. Failing to comply with regulations not only leads to hefty fines and legal consequences, but it can also damage a company’s reputation and trust with customers.  However, compliance shouldn’t be viewed as a mere checkbox exercise. It has the potential to bring significant benefits to a business, particularly in the long term. By implementing a compliance program that goes beyond what is required by regulations, companies can improve their overall operations and reduce the risk of non-compliance. 

Long-term benefits for the organizations :  

  1. Reduction / elimination of regulatory/ legal issues:   
    The regulations help protect your business, your employees, and your customers. For example, security regulations exist to help protect against data breach, financial regulations are there to protect against fraud, and safety regulations are designed to keep organizations safe. Failing to adhere to regulatory compliance requirements can open you up to risks beyond fines.
  2. Improve the Organizations Reputation & Reliability: 
    Compliance lays the foundation on which the organizations build their reputation and brand image. Regulatory compliance helps the organization to protect the business’s resources and reputation. It takes time to build trust with customers, prospects, and vendors, and a big part of that centers on the organization’s ethical behavior.  The public image of a business influences its success. Non-compliance-related issues and legal problems will tarnish a brand’s image, resulting in a loss of trust among the general public—Labour Law compliance and following the social responsibility help to uphold a positive image while building consumer loyalty.  Sometimes, all it takes is one compliance misstep leading the organization to tremble the trust it has built over years. By not following compliance regulations, the organization might even face the risk of losing access to certain segments of customer base. For example, if the organization violates HIPAA regulations, it could lose access to certain insurance companies or risk its license with the state.
  3. Improved Compliance culture enhances the Productivity level: 
    Though organizations might find it difficult to meet their compliance requirements, they are expected to conduct their business duly adhering to applicable laws, rules, and regulations, including meeting HR Compliance requirements. Secured connectivity ensures the employees will never be more than an arm’s length away from their laptop or tablet to complete their job.  Failing to maintain the standards set by the law and the rules governing the business will lead to Regulatory action / legal liability. It may also damage business reputation and negatively impact productivity. Non-compliance will drain away the precious time and effort of the employees in attending to the regulatory queries , providing data, attending legal cases.  Working in a fully compliant environment will have a direct impact on the productivity of the employees.
  4. Making the Organization as “Best place to work”: 
    Failing to adhere to regulatory compliance requirements can open organizations up to risks beyond just penalties/ fines.  These compliance regulations aren’t put in place to make life more difficult (although, in reality, they often do). But compliance with regulations benefits your company as well as internal and external individuals. In those organizations where there is appropriate governance structure, defined roles & responsibilities, data privacy is in place.
    An organization where the regulatory framework/ compliance management is automated under one roof, which ensures compliance to the regulations will be supplementing the efforts of existing resources, which in turn will attract skilled resources and retain the existing talent pool with the organization, enabling the organization to make the company as “Best Place to work”.
  5. Improves the market share:   
    A regulatory compliant organization, with appropriate Business Continuity & DR plan will be able to deliver the goods/ services to its customers, in the event of a disaster in the primary site, thereby able to retain satisfied customers and attract more business/market share.  Regulatory compliance is often considered an obstacle to innovation, but it’s a critical aspect of ensuring the success and scalability. Staying compliant makes the organization more efficient, increases productivity, and saves money—leading to increased profitability over time. It also enables the business by taking advantage of opportunities when they arise. Further, organizations can also expand into new markets because regulatory compliance is part of a global strategy that gives companies the confidence to do business across jurisdictions.
  6. Improves the bottom line:  
    When an organization fails to comply with applicable regulations, it leads to Regulatory penalties, potential lawsuits, financial liability all impacting the organization’s financials.  Cyber-attacks globally increased by 125% through 2021, and increasing volumes of cyber-attacks continued to threaten businesses and individuals in 2022. The rate and cost of data breaches are increasing. Since 2001, the victim count has increased from 6 victims per hour to 97, a 1517% increase over 20 years. It is pertinent to note that being a compliant organization is the base for building a successful, ever-growing organization. 

QRC’s Integrated Compliance and Audit services, along with the team of certified professionals, offer a unique approach to compliance that helps organizations achieve and maintain compliance. The comprehensive assessments provide a clear understanding of the risks associated with compliance, allowing organizations to make informed decisions about their operations. 

Moreover, by aligning business strategy with compliance risk strategy, QRC helps organizations create a culture of compliance, which not only mitigates risks but also enhances the overall effectiveness and efficiency of the organization.  QRC’s approach to compliance offers numerous benefits beyond mere regulatory compliance. By implementing a comprehensive compliance program, businesses can improve their overall operations and mitigate risks, ultimately paving the way for greater success.  

Let us assist you in achieving your compliance goals and driving your business forward. 

Future of Compliance- Trends and developments to watch

According to recent studies, organizations are shifting their approach to compliance risk management from treating it as a separate vertical to integrating it under operational risk management. This approach allows organizations to assess and measure risk based on residual risk, and focus on the most critical weaknesses. With increasing globalization and complex regulatory compliance requirements, managing compliance risk under the umbrella of operational risk has become essential. This integration also simplifies compliance testing, which can be a challenging task for many organizations.

Digital transformation : Factor-in the current and future trends

All organizations are seeking to get maximum value from their digital transformation. The Covid-19 pandemic has changed the way of business/operations, disrupting and giving opportunity to find new ways to face challenges by adopting to different business models, forcing to move to digitization, which means adoption of digital enablers like Artificial Intelligence (AI)- which includes Machine learning, Big data analytics, Robotic Process Automation (which requires Business Process Mapping to address overlapping process and creating process families), Internet of Things, Cloud/hybrid cloud, operating technology, augmented reality etc.

With a lot more efficiency coming into the system, regulators have also adopted these digital enablers. The above regulatory welcome change makes the corporates to improve and strengthen their compliance function using a more structured approach and digitization to avoid increasing penalties and fines (financial and non-financial) on non-compliance to regulations for their organizations as well as engaged 3rd parties. Although these enablers and technology are used in business growth and compliance, they usher in newer technology related risks, which must be mitigated. For example data/ information security and privacy related risks were not prominent earlier, they have become increasingly prominent in this age of digitization and have necessitated the need for Organizations to change and manage Compliance risk as newer regulations emerge from various regulators.

Data Privacy & security- another factor in the current and future trends

By year-end 2024, Gartner predicts that 75% of the world’s population will have its personal data covered under modern privacy regulations and predicts that large organizations’ average annual budget for privacy will exceed $2.5 million by 2024.

Adopting and implementing some cyber security related audit standards, using standard tools, certifications etc. have become the necessity of the day instead of just adopting these for regulatory purposes.

As an example- let us examine the context of the bank card end-to-end process. The process, if examined in depth, involves not only the Bank, but involves many 3rd party service providers such as card producers, payment gateway facilitators (which may be using cloud), settlement & reconciliation related facilitators etc. As these, 3rd parties may be in one jurisdiction or involve multiple jurisdictions, it becomes necessary to have the regulations driving this universe analyzed, audited under one umbrella- this task is extremely difficult.

Compliance requirements in the current environment moving rapidly to a digitized business environment

The technology operations (involving compliance to many regulations) require tools and audit to mitigate the risks. Organizations  use Security Operations Centre (SOC), Privilege Access Management (PAM), Network Access Management (NAM), Firewalls etc. for their IT infra and warrant the engaged technology 3rd parties to have these in place to mitigate risk and regulatory compliance. Further, using ISO framework/ NIST framework etc. strengthen the organizations to strengthen their IT infra with detailed audits for gaps and controls. Certifications of these agencies help the Organization to satisfy the regulator as well as retain their existing customer base. Additionally using tools like VAPT help organizations to assess the vulnerability and penetrations by rogue players against their IT infra defences  systems.

Data aggregation, data management, data analytics, data security etc. have assumed significant levels – although primarily one looks at these from an Operational risk perspective (which includes compliance risk), one requires to understand that above mentioned data related aspects accompany a lot of regulatory/global standards compliance requirements.

Some examples to address the above concerns on data/ information are say PCIDSS (on card data) HIPPA (for health records/ data of patients), GDPR (for personal data protections) etc. which are standards used globally.

QRC Services:

QRC Assurance and Solutions as an organization has worked extensively on addressing issues emerging from the current and future compliance requirements. Some of the audits/ tools provided by QRC Assurance and Solutions include:

– PCIDSS (Card Holder Data), HIPPA (ePHI), GDPR (PII) appropriately for Organizations to assess and address the gaps resulting from data security and privacy related at the People, Process and Technology of the organization as well as any engaged 3rd party providers.

– Conduct Audits on prescribed data security/ privacy standards by various regulators such as RBI, NABARD, IRDA, UIDAI, SEBI, SWIFT etc.

– Perform Vulnerability and Penetration Testing Scans using various techniques including Black box, Grey Box, White Box Testing.

– Perform configurations audits to assess the technology and systems related gaps.

QRC Assurance and Solutions offers QRCAssist, a centralized platform that provides effective compliance management System and Self-Assessment tool (SAT) to organizations to help them evaluate/ assess their status of Compliance vis-à-vis various standards/ regulations.